

International Privacy Training for Customer Support Teams
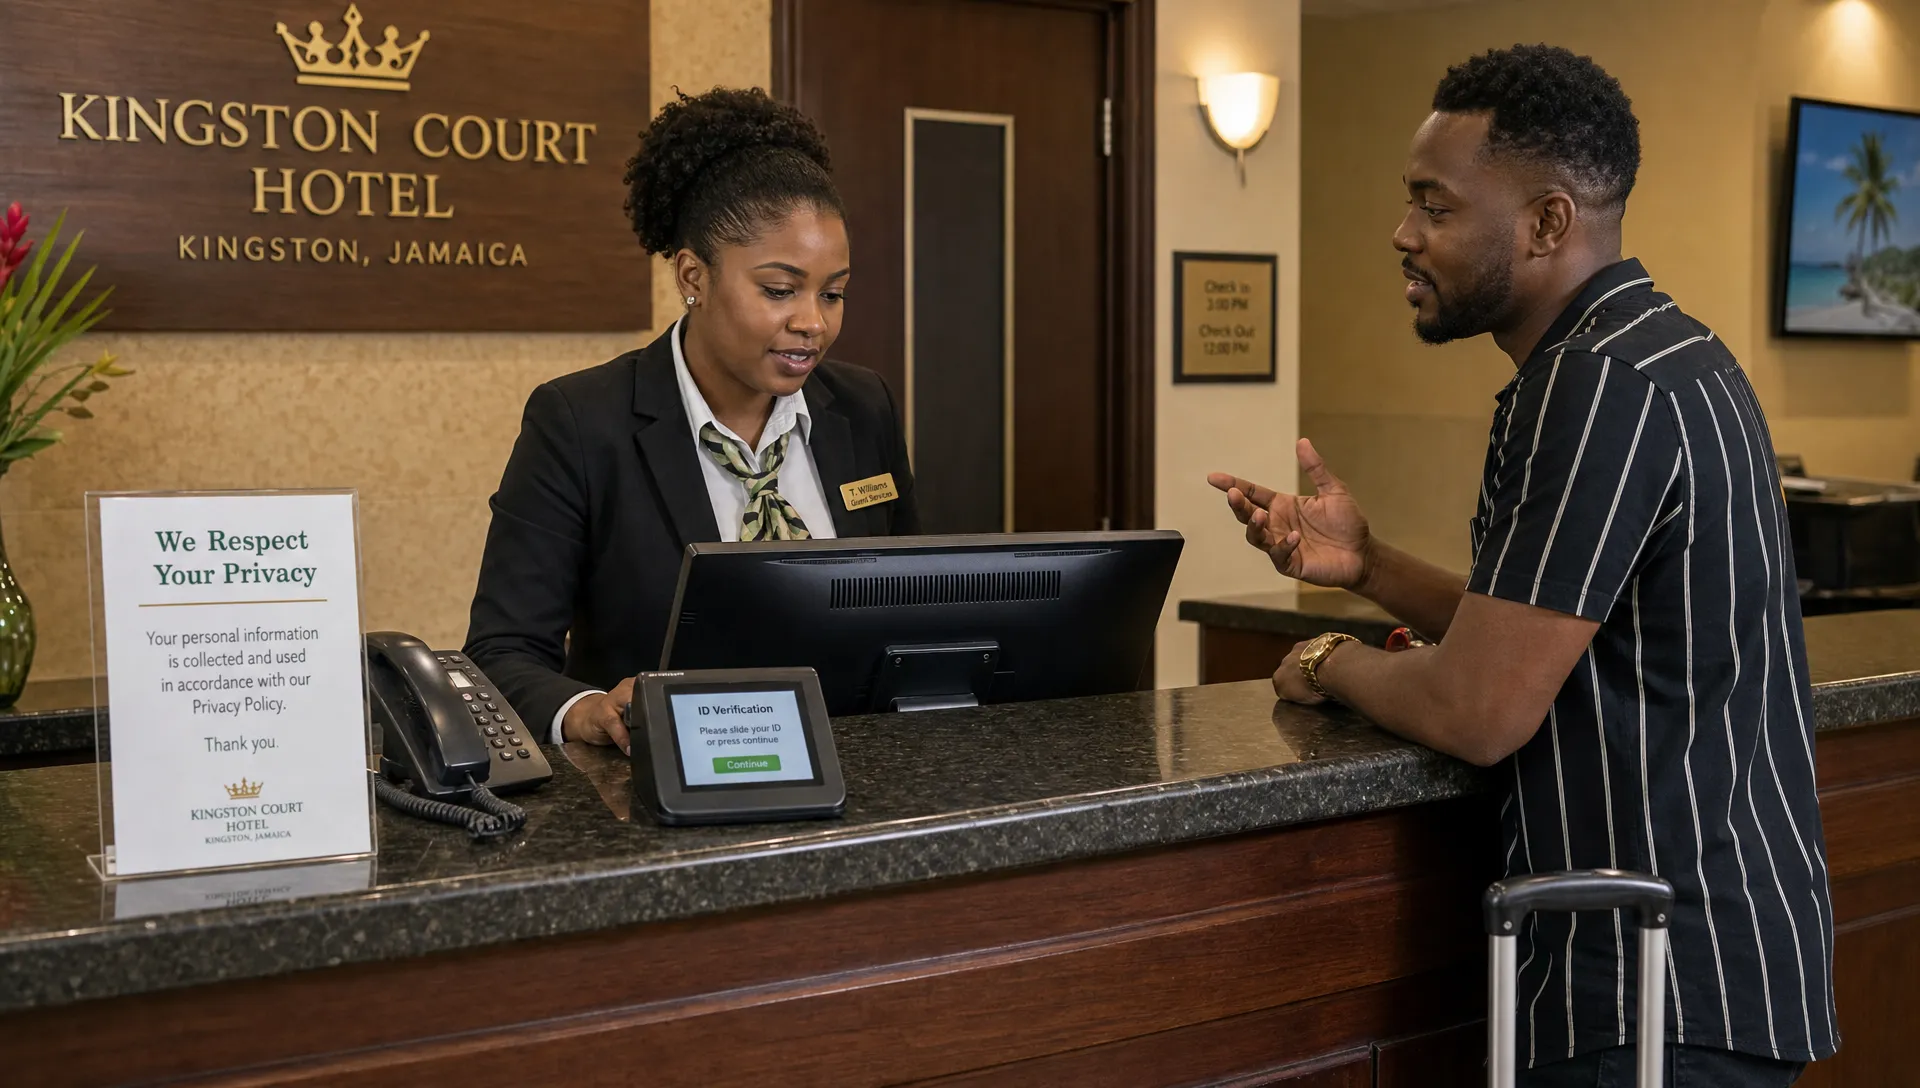
International privacy training for customer support teams is now a practical compliance requirement, not a generic awareness exercise. Customer support agents answer questions, verify identities, update account records, process complaints and sometimes handle frustrated customers in real time. That makes them one of the most important privacy control points in any organisation, especially when a Jamaican team supports customers across multiple countries.
For contact centres, BPOs, financial services firms, hospitality groups, healthcare providers, ecommerce businesses and technology companies, the risk is not only whether staff know the law. The real test is whether they know what to say, what not to say, what to record and when to escalate. A well designed programme connects privacy principles to the exact conversations support teams have every day.
Why Customer Support Teams Need an International Privacy Lens
Customer support teams often sit at the intersection of data protection, customer experience and operational risk. They work with names, addresses, identification details, payment issues, complaints, account histories, call recordings and CRM notes. In regulated sectors, they may also handle information tied to anti-money laundering checks or customer due diligence.
This is why support training should not be copied from a general staff privacy presentation. It should be role-specific, scenario-based and aligned with the jurisdictions your customers, vendors and group companies operate in. PLMC has written separately about why training should be tailored for HR, IT and customer-facing teams, and customer support deserves particular attention because privacy decisions happen while the customer is waiting.
Jamaican Compliance Is the Starting Point, Not the Limit
For Jamaican organisations, the Data Protection Act 2020 provides the baseline for data protection compliance. The Office of the Information Commissioner is the key regulator, and organisations should treat Jamaica data privacy obligations as part of everyday operations rather than a one-off legal project.
The Act includes principles that are directly relevant to support work, such as fair processing, specified purposes, accuracy, retention, security and safeguards for transfers outside Jamaica. Support teams do not need to memorise every section of the law. They do need to understand what those standards mean when a caller asks for someone else’s account information or a customer asks for deletion of their records.
International Support Creates Extra Risk
Many Jamaican teams support customers in the United States, Canada, the United Kingdom, the European Union and across the Caribbean. The phrase GDPR Jamaica often reflects a practical question: if our team is in Jamaica but our customer is in Europe, what should our agents know?
The answer depends on the organisation’s role, customer base, contracts, data flows and applicable laws. The European Commission’s overview of EU data protection rules is a useful reference point, but the support team does not need a law school lecture. It needs clear scripts and escalation rules for international privacy requests.
What International Privacy Training for Customer Support Teams Should Cover
A strong programme should translate legal requirements into support behaviours. International privacy training for customer support teams should answer four practical questions: what data can we collect, how do we verify identity, when can we disclose information and who handles requests that go beyond routine service?
Recognising Personal Data in Support Channels
Support teams should know that personal data is not limited to names and ID numbers. It may include email addresses, phone numbers, booking references, IP addresses, account notes, complaint details, voice recordings and combinations of data that identify a person indirectly.
This matters because support agents often work across channels. A chat transcript, call recording, WhatsApp message, email attachment and CRM note may all contain personal data. Training should help staff spot sensitive information before it is copied, shared or stored in the wrong place.
Identity Verification Without Overcollection
Customer support teams must verify identity before releasing account information, but verification can become risky when staff ask for more information than necessary. Training should define approved verification steps for each support channel and customer type.
For example, a support agent may be allowed to confirm selected account details but not request a full copy of identification unless the process requires it. If a caller fails verification, the agent should know how to continue politely without disclosing information that confirms whether the account exists.
Privacy Scripts for Real Conversations
Scripts should not make support agents sound robotic. Their purpose is to reduce improvisation when privacy risk is high. Teams need approved wording for common situations such as third-party callers, account access requests, complaints about consent, marketing opt-outs, data correction requests and suspected fraud.
A useful script gives agents three things: a compliant answer, a clear next step and a point of escalation. It should also explain what not to say, since overpromising deletion, access or compensation can create legal and customer experience problems.
A Jurisdiction Map for Support Training
International privacy training should not try to teach every global privacy law in detail. A better approach is to build a practical jurisdiction map that shows which rules matter to the support team and what behaviour those rules require.
Jurisdiction or framework | What support teams should recognise | Practical support behaviour |
Jamaica Data Protection Act 2020 | Personal data, processing standards, individual rights and cross-border transfer concerns | Collect only what is needed, follow approved retention rules and escalate rights requests |
EU GDPR | Rights requests, lawful handling, transparency and possible extraterritorial reach | Do not promise immediate outcomes, log the request and route it to the privacy lead |
UK data protection rules | Similar operational expectations for transparency, rights and accountability | Use approved scripts for UK customers and preserve records of the interaction |
US state privacy laws | Varying consumer rights, opt-outs and sensitive data expectations | Identify the customer location and use the correct escalation path |
Contractual client requirements | Client-specific security, reporting and handling rules | Follow the client playbook and escalate any conflict with local procedures |
Anti-money laundering obligations | KYC, suspicious activity indicators and regulated customer due diligence | Do not bypass verification, and route AML concerns to the authorised compliance function |
The map should be short enough for team leads to use during coaching. Legal and compliance teams can maintain the underlying detail, but front-line employees need a version that supports fast, consistent decisions.
Customer Support Scenarios That Staff Should Practise
Privacy training becomes useful when agents practise realistic moments. A support team that serves international customers should rehearse scenarios where privacy, urgency and customer emotion collide.
Good scenarios include a spouse requesting account details, a parent calling about an adult child, a customer asking for all records held about them, a caller demanding immediate deletion, a suspected fraudster trying to reset an account and a customer sending identification documents through an unapproved channel.
Teams should also practise internal scenarios. For instance, can one agent send a screenshot of a customer record to a colleague over personal messaging? Can a team leader export complaint logs to a spreadsheet? Can support use real customer cases in training? The answers should be built into procedures, not left to individual judgement.
How to Deliver Training for Distributed Support Teams
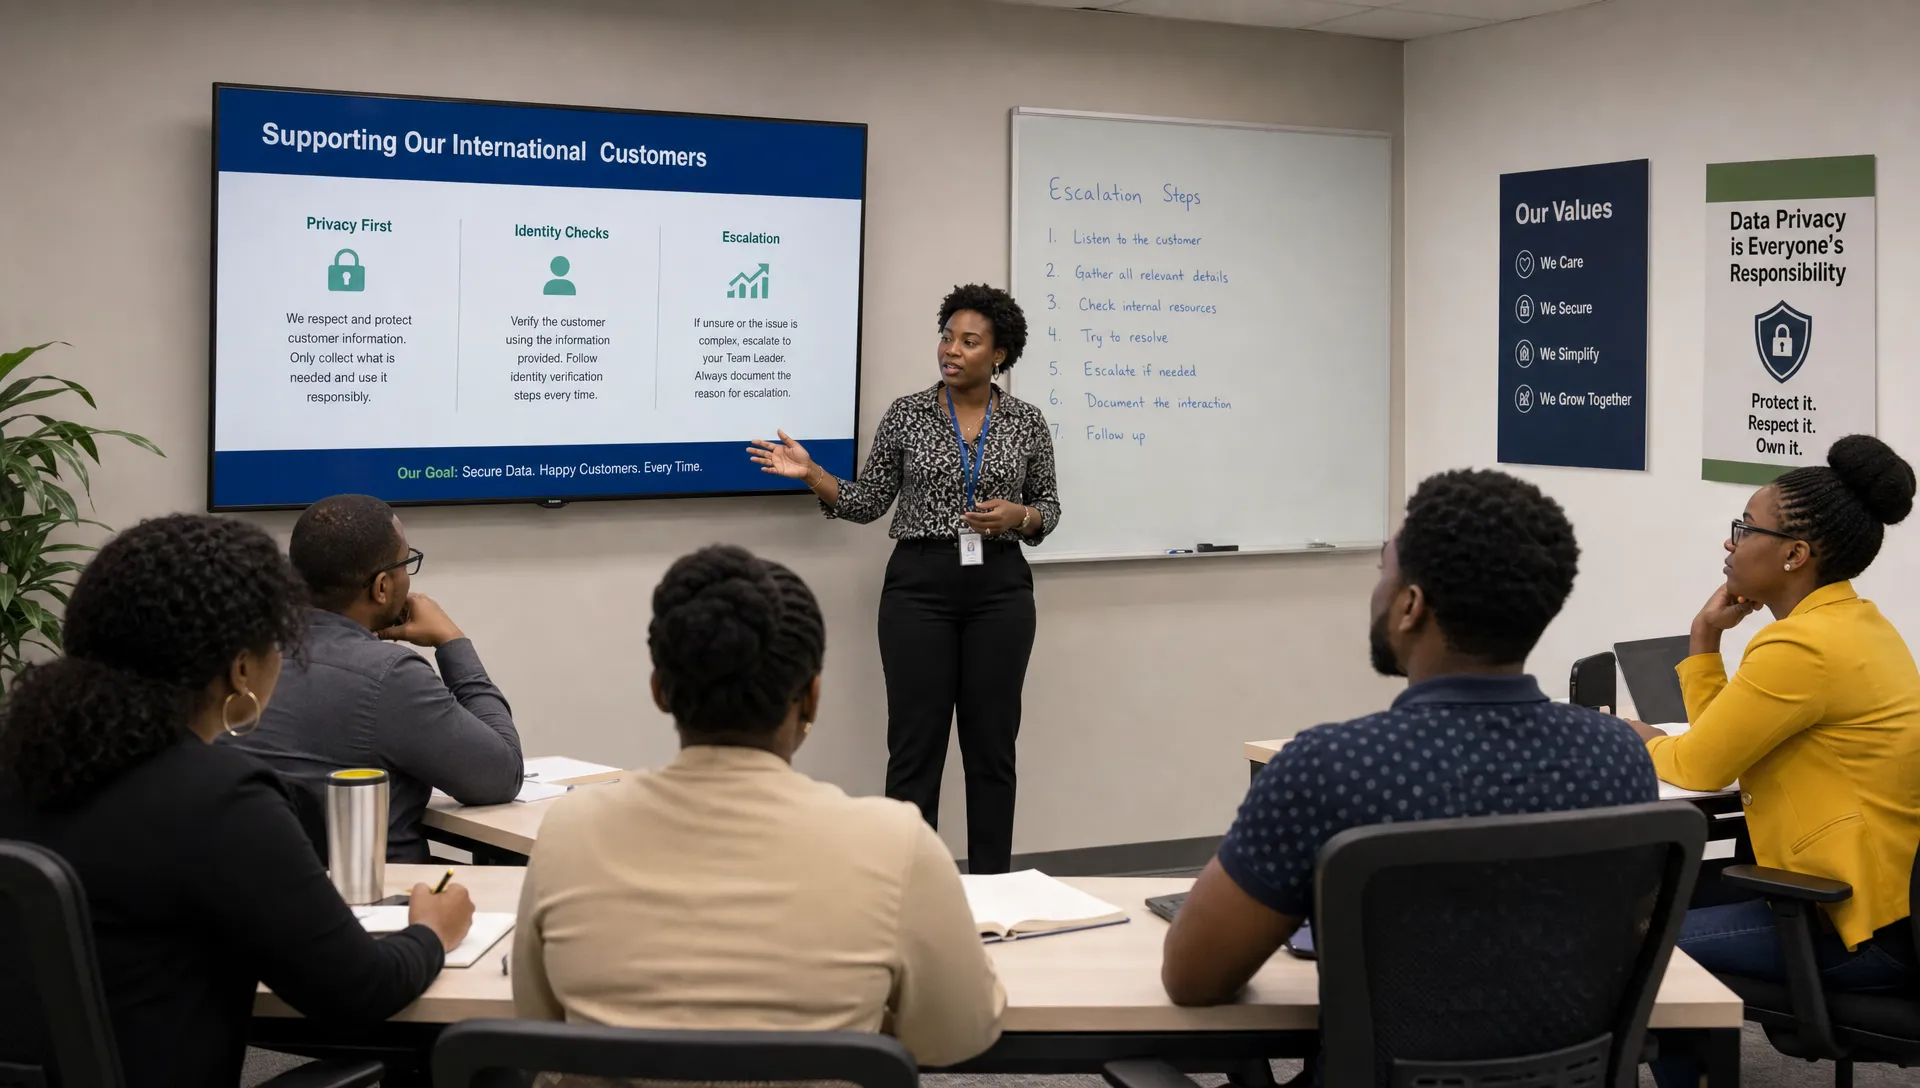
Many support teams operate across shifts, locations and time zones. Some work remotely. Others are outsourced or blended with client-side staff. A single annual session is rarely enough for this environment.
The most effective structure combines onboarding, short refreshers and targeted coaching. New starters need privacy training before they handle live customer data. Existing agents need refreshers when scripts, systems, laws or client requirements change. Supervisors need deeper training because they review escalations and influence team behaviour.
Short sessions can work well when they focus on a single behaviour. PLMC has covered practical formats for short data protection awareness training for busy teams, which is especially relevant for customer support environments where taking agents off queue has a real operational cost.
A Practical Training Sequence
For organisations comparing data privacy training Jamaica options, the best programme is usually a sequence rather than one long presentation. A practical sequence may include:
Foundation module: Personal data, privacy principles, Jamaica data privacy obligations and why support teams are high risk.
Channel module: Handling personal data in calls, emails, live chat, CRM notes, messaging apps and call recordings.
Verification module: Approved identity checks, failed verification rules and third-party caller scenarios.
International module: How to identify customer location, recognise GDPR-related requests and follow client-specific rules.
Escalation module: Rights requests, complaints, breaches, suspected fraud and anti-money laundering concerns.
The sequence should be supported by job aids, not just slides. A one-page escalation guide often changes behaviour more reliably than a long policy document.
Building Scripts, Job Aids and Escalation Rules
A privacy training programme should leave behind tools that supervisors can use every week. Scripts, checklists and escalation matrices help make the training operational.
Support scripts should cover account access, authentication failure, marketing opt-outs, data correction, data access requests, deletion requests, complaints about consent and customers asking how their information is used. Each script should be reviewed by privacy, legal, compliance and operations before use.
Escalation rules should be simple. If a request relates to legal rights, suspected unauthorised disclosure, law enforcement, media enquiries, regulators, litigation, AML issues or a client-specific contractual requirement, the agent should not resolve it alone. The agent should log the matter and route it to the approved function.
What Supervisors Should Monitor
Supervisors are essential to data protection compliance because they turn training into habits. They should review call quality, CRM notes, authentication steps, complaint handling and escalation timeliness.
Quality assurance forms should include privacy criteria. If quality reviews only measure friendliness and resolution time, agents may learn that privacy slows them down. A balanced scorecard should reward safe handling, accurate logging and correct escalation.
Measuring Whether the Training Works
Training attendance is not proof of competence. Organisations should measure whether support agents apply privacy rules during real work.
Useful measures include the percentage of agents completing onboarding before system access, quality review scores for verification, the number of privacy escalations logged, repeat issues by team, time taken to escalate potential incidents and reduction in avoidable handling errors. These measures should be used for improvement, not blame.
If your organisation is designing a broader programme, it may help to start with the behaviours you want staff to apply. PLMC’s guide on planning data protection training that staff will apply explains how to move from policy content to workplace action.
Keep Evidence for Governance
Training records matter for corporate governance. Boards, senior management, auditors, clients and regulators may all ask how the organisation ensures staff understand privacy obligations.
Evidence should include attendance records, training materials, assessment results, role-based training schedules, script approvals, refresher dates and records of coaching after incidents. For outsourced support operations, contracts should also define training responsibilities, reporting expectations and audit rights.
Common Mistakes to Avoid
One common mistake is treating international privacy as a legal topic only. If training focuses on statutes but ignores call handling, staff may understand the theory yet fail in the moment.
Another mistake is giving agents too much discretion. Customer support teams need empathy and judgement, but they should not decide legal rights requests, regulator enquiries or breach notifications on their own.
A third mistake is training only employees while ignoring contractors, temporary agents and outsourced partners. If they access customer personal data, they need appropriate training and supervision. Privacy risk follows the data, not the payroll category.
Finally, some organisations forget to update training after process changes. A new CRM field, chatbot, call recording tool, identity verification vendor or cross-border client can change the privacy risk profile quickly.
Frequently Asked Questions
What is international privacy training for customer support teams? It is role-based training that teaches support agents how to handle personal data when serving customers across countries, channels and legal frameworks. It usually covers verification, data minimization, scripts, rights requests, escalation and jurisdiction-specific handling rules.
Do Jamaican customer support teams need GDPR training? They may need GDPR awareness if they serve EU or UK customers, support a client subject to GDPR or handle personal data under contracts that require GDPR-aligned controls. The level of training should match the team’s actual responsibilities and risk exposure.
How often should customer support teams receive privacy training? New agents should be trained before accessing live customer data. Existing teams should receive at least periodic refreshers, with additional training when systems, scripts, customer markets, client contracts or legal requirements change.
Should privacy training include anti-money laundering topics? It should include AML touchpoints where support staff handle identity checks, account changes, suspicious activity indicators or regulated customer interactions. The privacy programme should not replace AML training, but both should be aligned so agents understand verification and escalation duties.
What should be documented after training? Organisations should keep attendance records, training materials, assessment results, role-based schedules, approved scripts, escalation procedures and evidence of coaching. These records support governance, audits, client assurance and data protection compliance.
Strengthen Your Support Team’s Privacy Readiness
Customer support is where privacy policies become real. If your agents are unsure how to verify identity, handle international requests or escalate potential incidents, the organisation is carrying avoidable risk.
Privacy & Legal Management Consultants Ltd. supports Jamaican organisations with data protection implementation, compliance training, corporate governance, cyber security and wider GRC integration. To discuss a practical training programme for your customer support environment, visit Privacy & Legal Management Consultants Ltd. and request guidance tailored to your operations.