GDPR Readiness for Jamaican Service Providers
For many Jamaican service providers, the GDPR is no longer a distant European rule. It comes up in vendor questionnaires, outsourcing agreements, tourism partnerships, software contracts, BPO proposals, professional services engagements and cross-border data sharing arrangements.
A European client may not ask for a legal essay. They will ask whether you can prove that personal data is handled securely, lawfully and in line with their own obligations. That is the practical meaning of GDPR readiness for Jamaican service providers: not claiming perfect compliance, but showing that your governance, contracts, controls and evidence are ready for scrutiny.
This matters even where your organisation is already working on Jamaica’s Data Protection Act, 2020. Local compliance is a strong foundation, but GDPR readiness adds another layer when EU personal data, EU-based clients or international procurement standards enter the picture.
When the GDPR can matter to a Jamaican service provider
The General Data Protection Regulation applies directly across the European Union, but its influence travels through contracts and supply chains. A Jamaican organisation may encounter GDPR obligations in several ways.
First, an EU organisation may appoint a Jamaican company as a processor. This is common where a Jamaican provider delivers customer support, software maintenance, hosting support, payroll processing, analytics, claims administration, reservations handling or back-office services. In that relationship, the EU client remains responsible for choosing processors that provide sufficient guarantees, and the Jamaican provider will usually have GDPR duties written into the contract.
Second, a Jamaican business may directly offer services to people in the EU or monitor their behaviour. The official GDPR text includes territorial scope rules that can bring some non-EU organisations within the regulation where their activities are directed at individuals in the EU.
Third, a Jamaican company may sit in a larger chain as a subprocessor. For example, a Caribbean service centre may support a US or UK technology vendor that serves EU customers. The EU client may never contract with the Jamaican provider directly, but GDPR requirements can still flow down through the main vendor’s contract.
Commercial expectations often go further than strict legal scope. EU and UK clients increasingly run privacy due diligence before onboarding suppliers, especially where personal data is sensitive, large-scale or business-critical. A provider that can answer those questions clearly has an advantage over one that treats privacy as a last-minute legal formality.
For a broader cross-border view, PLMC has also explained the international privacy rules Jamaican businesses cannot ignore, including foreign law triggers that may affect Jamaican organisations.
GDPR readiness is not the same as Jamaica DPA compliance
Jamaica’s Data Protection Act, 2020 is the starting point for Jamaican organisations. It helps build the core disciplines that international clients expect: accountability, lawful processing, transparency, security, retention controls and respect for individual rights. If your team needs a local baseline first, PLMC’s guide to the Jamaica Data Protection Act for businesses is a useful place to begin.
However, GDPR readiness asks additional questions. Can you sign an EU-style data processing agreement? Can you support transfer assessments? Can you identify subprocessors? Can you assist an EU controller with data subject requests, breach notifications and deletion instructions? Can you produce evidence, not just policies?
The table below shows how the two compliance conversations often connect.
Readiness area | Jamaica DPA foundation | GDPR readiness question |
Governance | Who is accountable for personal data handling? | Can the client identify a privacy contact, escalation path and decision owner? |
Data inventory | What personal data is collected, used, stored and shared? | Can EU data flows be separated, mapped and explained? |
Lawful processing | Why does the organisation process personal data? | Is the Jamaican provider following the controller’s documented instructions? |
Contracts | Are third parties managed responsibly? | Does the agreement include Article 28 processor terms and subprocessor controls? |
Security | Are appropriate technical and organisational measures in place? | Can the provider evidence access controls, encryption, incident response and staff training? |
Transfers | Is personal data shared outside Jamaica? | Is there a lawful EU transfer mechanism, such as Standard Contractual Clauses? |
The overlap is helpful, but it should not create complacency. GDPR-related work must be tailored to the specific service, the client’s role, the data involved and the jurisdictions in the chain.
Start with role clarity and data flow mapping
The first readiness step is not buying software or copying a European policy template. It is understanding your role. A Jamaican service provider may be a processor for client data, a controller for employee data and a joint decision-maker in a separate partnership. Each role carries different duties.
A BPO handling customer service tickets for an EU retailer will usually act as a processor for that retailer’s customer data. A Jamaican consultancy that independently decides how to use attendee information for its own events may be a controller for that activity. A software provider may be a processor for customer content but a controller for billing, marketing and account administration.
This is why data flow mapping is so important. It turns vague statements into operational facts. You need to know what data enters your organisation, where it comes from, who accesses it, which systems store it, which vendors support it, how long it is retained and how it is returned or deleted.
Mapping question | Why it matters for readiness | Evidence to keep |
Whose personal data is processed? | Identifies whether EU data subjects are involved | Client onboarding forms, data inventories, project scopes |
What categories of data are involved? | Flags sensitive data, children’s data or high-risk processing | Data classification records, risk assessments |
Which systems are used? | Shows where data is stored and who can access it | System register, access matrix, cloud vendor list |
Who are the subprocessors? | Supports contractual approval and transparency | Subprocessor register, vendor due diligence records |
Where is data accessed from? | Supports transfer analysis and security planning | Access logs, location records, remote work controls |
What happens at contract end? | Supports return, deletion and retention obligations | Retention schedule, deletion certificates, exit checklist |
Good mapping also prevents overcommitment. If a client asks whether EU data is segregated, retained for a defined period or accessible only by approved staff, your answer should come from records, not memory.
Core controls EU clients expect to see
GDPR readiness for Jamaican service providers is built around controls that can be explained, tested and evidenced. The controls do not have to look identical in every organisation. A small professional services firm and a large outsourcing centre will not have the same risk profile. Still, the core themes are consistent.
Contract terms that match the service
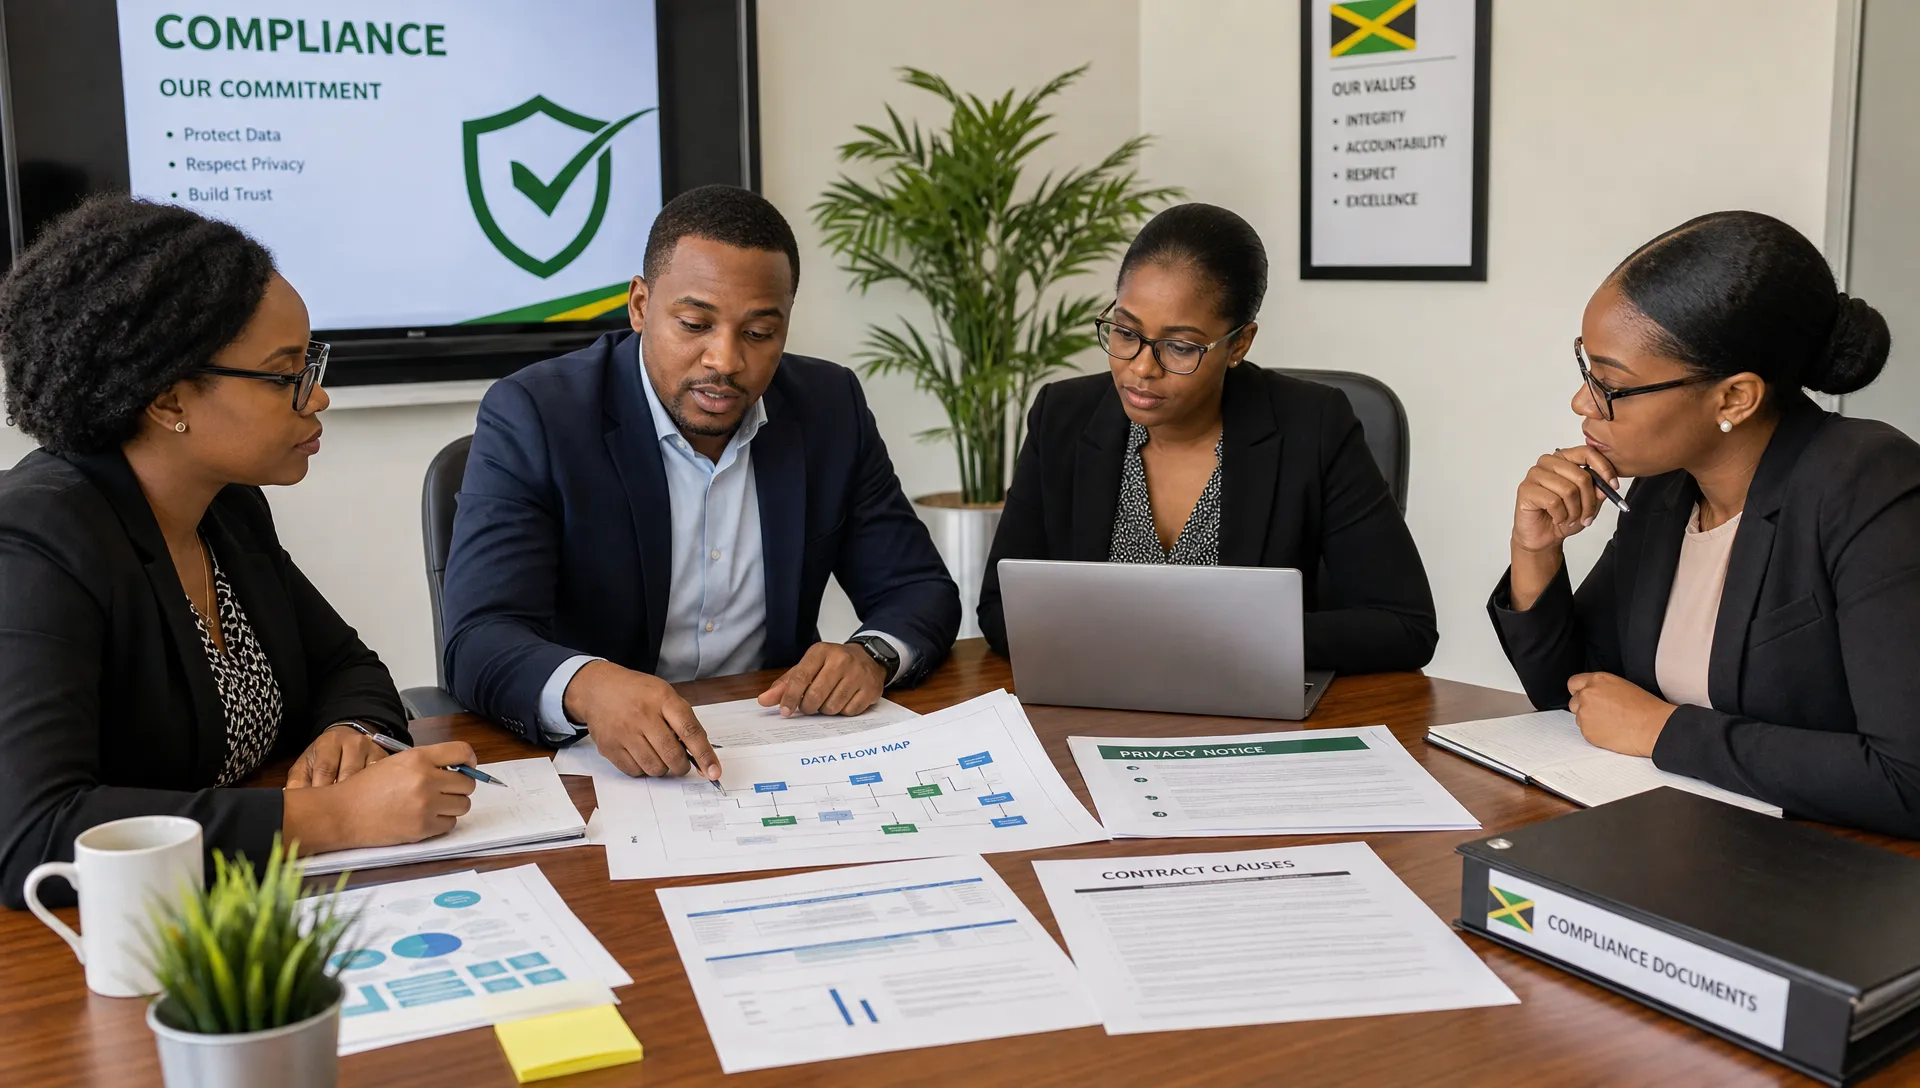
For processor relationships, EU clients commonly require a data processing agreement. Under GDPR Article 28, processor terms typically address documented instructions, confidentiality, security measures, subprocessor approval, assistance with data subject rights, breach support, deletion or return of data and audit rights.
Do not treat these clauses as boilerplate. If the contract says data will be deleted within a defined period after termination, your operations team must know how to do that. If the agreement requires prior notice before adding a subprocessor, procurement must not onboard new tools informally. If audit rights are included, someone must know where the evidence is kept.
Security controls that can be demonstrated
Security is often the area clients test most closely. They may ask about multi-factor authentication, access reviews, encryption, device management, vulnerability management, backup practices, logging, physical security and incident response. You do not need to disclose sensitive security details that create risk, but you should have a structured way to answer due diligence questions.
Cybersecurity should not be treated as an IT-only matter. Privacy, legal, operations, HR and management all have roles. Staff need to understand phishing risks, clean desk practices, confidentiality duties, approved communication channels and escalation steps when something goes wrong.
Procedures for individual rights and client assistance
A Jamaican processor may not respond directly to every EU data subject request, but it must be able to help the controller. If an EU client receives a deletion, access, correction or restriction request, the provider may need to locate records, export information, suppress processing or delete data from active systems and backups according to agreed procedures.
The risk is delay. GDPR timelines can be tight for controllers, so processors must know how to recognise requests and escalate them quickly. Front-line staff should not improvise answers or ignore privacy-related messages because they are unsure what to do.
Breach response and notification support
A personal data breach is not limited to hacking. It can include misdirected emails, unauthorised access, lost devices, accidental deletion, ransomware, exposed cloud storage or improper disclosure to a third party. GDPR requires controllers to assess breaches quickly, and processors must notify controllers without undue delay after becoming aware of a breach.
That means your internal procedure should define what staff must report, who receives the report, how incidents are triaged, how evidence is preserved and who communicates with the client. A tabletop exercise is often more useful than a policy that no one has tested.
International transfers need special attention
When EU personal data is transferred to Jamaica, transfer safeguards are usually central to the GDPR conversation. Jamaica is not currently listed by the European Commission as a country with an EU adequacy decision. The Commission maintains its adequacy decision information publicly, and clients may check it during due diligence.
In many cases, EU organisations rely on Standard Contractual Clauses for transfers to service providers in non-adequate countries. The relevant module depends on the relationship, such as controller to processor or processor to processor. The SCCs are not just a signature exercise. They require practical cooperation, accurate descriptions of processing and appropriate technical and organisational measures.
Transfer impact assessments may also come up. After the Schrems II judgment, EU exporters generally need to assess whether the transfer tool works effectively in practice and whether supplementary measures are needed. A Jamaican provider may be asked to supply information about applicable laws, access controls, encryption, government access procedures, data locations and onward transfers.
From a readiness perspective, prepare a transfer pack that can be updated for each client. It should describe where data is stored, who can access it, which subprocessors are involved, what security controls protect it and how the organisation handles legally binding access requests if they arise. If your answers are scattered across teams, client onboarding will be slower and less consistent.
A practical 90-day readiness plan
GDPR readiness does not have to start with a massive programme. For many Jamaican service providers, a focused 90-day sprint can create the evidence base needed for client discussions. The timing below is a practical planning guide, not a legal deadline.
Period | Main objective | Practical output |
Days 1 to 15 | Confirm scope and roles | List EU clients, services, systems, data categories and controller or processor roles |
Days 16 to 30 | Map data flows and gaps | Data flow map, subprocessor register, risk notes and missing evidence list |
Days 31 to 50 | Strengthen contracts and transfers | Data processing agreement template review, SCC support pack, vendor due diligence checks |
Days 51 to 70 | Improve operational controls | Incident procedure, rights request escalation process, retention and deletion workflow |
Days 71 to 90 | Train, test and evidence | Staff training records, tabletop exercise notes, management sign-off and client due diligence pack |
The final pack should be simple enough for business teams to use. It can include a short privacy governance overview, a data flow summary, a security controls summary, a subprocessor list, incident response contacts, training records and sample evidence. Where a client requests deeper proof, you can provide it through an agreed due diligence channel.
PLMC’s article on how to prepare for a data protection audit in Jamaica is also relevant here, because the discipline is similar: define the scope, gather evidence, reconcile records and test whether policies work in practice.
Common readiness gaps to fix early
Many providers only discover GDPR gaps when a contract is already being negotiated. By then, the commercial team is under pressure and the privacy team is trying to catch up. These issues are worth addressing before the next proposal lands.
Saying the organisation is GDPR compliant without evidence to support the claim.
Signing processor clauses that operations cannot meet.
Failing to identify all cloud tools, subcontractors and informal workarounds used by staff.
Treating data retention as a policy statement rather than a system-level process.
Forgetting that breach response requires fast internal reporting, not just technical investigation.
Training senior staff but leaving front-line employees unsure how to recognise privacy requests or incidents.
A good readiness programme turns these weak points into routine controls. It also creates confidence. Sales teams can answer buyer questions more quickly, legal teams can negotiate from a clearer position and operational teams know what they are expected to do.
How to present readiness to EU clients
A polished policy is not enough. EU clients want assurance that privacy controls are active. The most effective approach is to present readiness in a way that matches procurement, legal and security review processes.
Start with a concise overview of your service, role and data handling model. Avoid generic claims. Explain whether you act as a processor, what services you provide, what categories of personal data you handle, where the data is hosted or accessed and what subprocessors support the service.
Then provide evidence at the right level. A client may not need your full incident response manual at the first stage, but they may need confirmation that a tested procedure exists. They may not need every security configuration detail, but they may need assurance on access control, encryption, staff confidentiality and breach escalation.
Finally, keep the pack current. GDPR readiness is not a one-time file saved for future tenders. It should be reviewed when services change, new systems are adopted, a new subprocessor is engaged, a breach occurs or a client expands the scope of work.
Frequently Asked Questions
Does the GDPR apply to every Jamaican service provider? No. The GDPR does not automatically apply to every Jamaican organisation. It becomes relevant where the provider processes EU personal data for an EU client, offers services to individuals in the EU, monitors individuals in the EU or is contractually required to meet GDPR-style obligations in a supply chain.
Is compliance with Jamaica’s Data Protection Act enough for EU clients? It is an important foundation, but it may not be enough on its own. EU clients may also require GDPR processor clauses, Standard Contractual Clauses, transfer information, subprocessor controls and evidence of operational procedures.
Do Jamaican providers need an EU representative? It depends on whether the organisation is directly subject to the GDPR under its extraterritorial scope rules and whether any exception applies. This should be assessed based on the specific service, target market and processing activity.
Can Standard Contractual Clauses solve all transfer issues? SCCs are a key transfer tool, but they are not a complete readiness programme. Clients may also require transfer impact information, security measures, subprocessor transparency and proof that the contractual commitments are operationally realistic.
How often should GDPR readiness be reviewed? Review it at least annually and whenever there is a material change, such as a new EU client, new system, new subprocessor, new data category, new service line or security incident.
Build client trust before the questionnaire arrives
GDPR readiness for Jamaican service providers is a business discipline as much as a legal one. It helps organisations compete for international work, reduce contract friction and show that personal data is being handled with care.
Privacy & Legal Management Consultants Ltd. supports Jamaican organisations with data protection implementation, governance, risk management, cybersecurity, anti-money laundering compliance, training and integrated GRC support. If your team is preparing for EU client due diligence or needs to strengthen its privacy evidence base, you can start with a free consultation with PLMC.