A Board Checklist for Cross-Border Privacy Risk
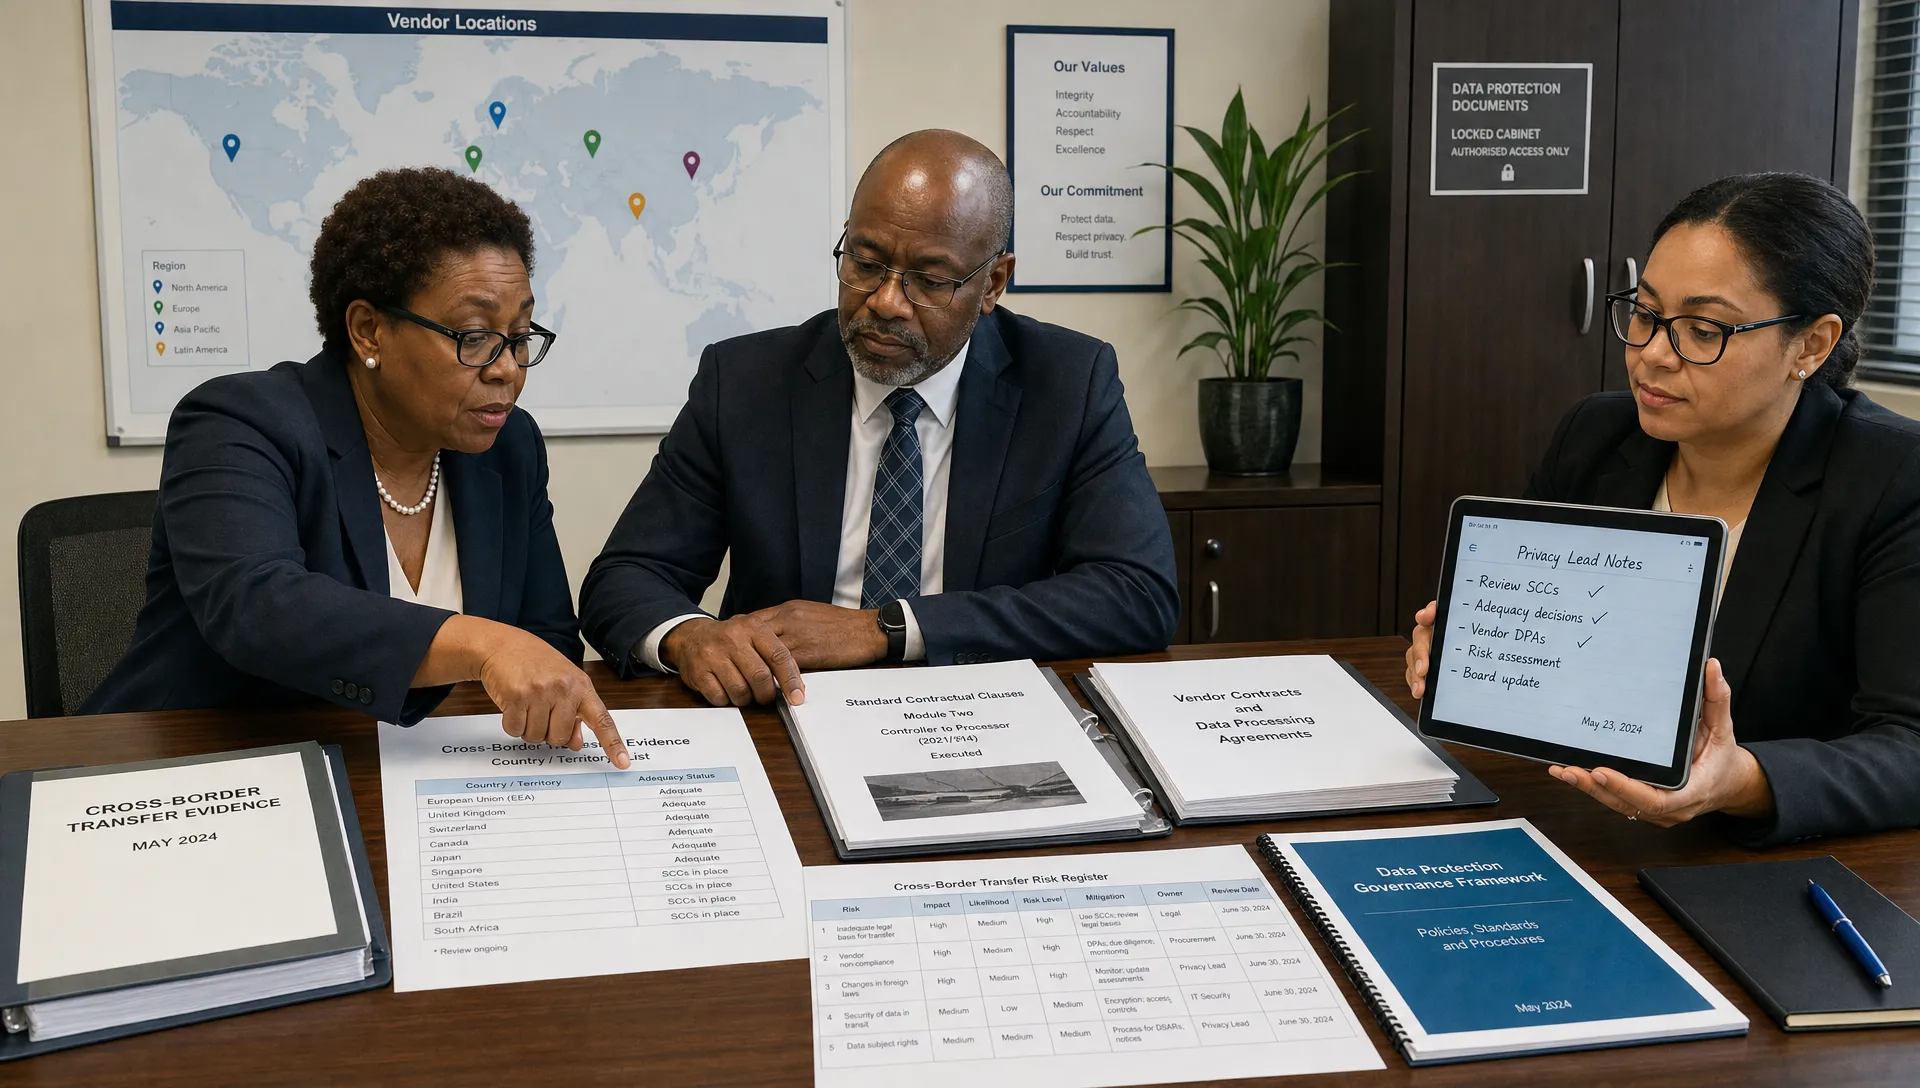
Cross-border processing is now routine for Jamaican organisations, from cloud hosting and payroll platforms to overseas group companies, payment processors and professional advisers. A board checklist for cross-border privacy risk should help directors move beyond general comfort statements and ask whether data protection, privacy and cyber controls are actually evidenced before personal data leaves Jamaica.
For boards, the issue is not only legal compliance. Cross-border transfers can affect customer trust, regulatory exposure, contract negotiations, merger value, operational resilience and reputational risk. Under Jamaica's Data Protection Act, 2020, organisations must be able to show that personal data is handled fairly, lawfully, securely and with appropriate accountability. When data moves into another jurisdiction, that accountability does not move with it.
Why cross-border privacy risk belongs on the board agenda
Directors do not need to approve every file transfer or every software configuration. They do need to oversee whether management has a defensible framework for identifying, assessing and controlling international data flows. That is especially important in sectors such as financial services, healthcare, education, tourism, telecoms, retail, BPO and professional services, where personal data often moves through multiple vendors and platforms.
The Office of the Information Commissioner is the key Jamaican regulator for the Data Protection Act, 2020. The Act includes data protection standards that require organisations to process personal data securely and to consider protections when transferring data outside Jamaica. If a breach, complaint or customer audit occurs, the board will want to know that management can produce more than a contract and a spreadsheet.
Cross-border privacy risk also overlaps with cyber security, corporate governance, anti-money laundering controls and enterprise risk management. A weak overseas processor can expose identity documents, transaction histories, employee records or customer profiles. A vague intra-group sharing arrangement can leave the organisation unable to explain who controls the data, who responds to rights requests and who is responsible when something goes wrong.
A board checklist for cross-border privacy risk
Use this checklist as a board agenda tool, not as a one-time compliance form. It is designed to help directors challenge management, request evidence and decide when a deeper data protection assessment is required.
Board question | Evidence to request | Red flag |
Do we know which personal data leaves Jamaica? | Data map, vendor register, system inventory and business owner list | Management cannot identify countries, vendors or data categories |
Is there a clear business purpose for each transfer? | Processing purpose, lawful basis and retention rationale | Transfers happen because a tool was convenient, not because it was assessed |
Have transfer safeguards been assessed? | Contract clauses, due diligence file, legal review and security assessment | Reliance on standard vendor terms with no review |
Are vendors and sub-processors controlled? | Processor agreement, sub-processor list and audit rights | Vendors can change sub-processors without notice or meaningful controls |
Is high-risk data treated differently? | Risk rating for sensitive data, children’s data, financial data and identity documents | All transfers are approved using the same low-risk process |
Can we respond to incidents across jurisdictions? | Incident response plan, notification workflow and vendor escalation contacts | Breach reporting depends on informal email chains |
Are overseas legal obligations monitored? | Register of applicable laws, customer commitments and GDPR exposure analysis | Management assumes Jamaican law is the only relevant law |
Does the board receive useful metrics? | Quarterly dashboard, exceptions, overdue actions and risk acceptance decisions | Reports say compliant without evidence or trend data |
A board checklist for cross-border privacy risk should be owned by management, reviewed by legal, privacy and information security leads and reported through the board risk or audit committee. If your organisation already runs quarterly risk discussions, it can be built into the broader cycle described in PLMC's guide to privacy risk reviews every board should schedule.
1. Know what leaves Jamaica, where it goes and why
The first board question is simple: can management show where personal data goes? Many organisations underestimate transfers because they only think about obvious outsourcing arrangements. In practice, cross-border processing may occur through cloud backups, analytics tools, customer relationship management systems, email marketing platforms, help desks, payroll providers, payment gateways, overseas consultants and group reporting systems.
The board should ask for a current map of international data flows. It does not need to list every individual data field, but it should identify the system, business owner, vendor, destination country, category of data subject, type of personal data, purpose, retention period and whether sub-processors are involved.
This exercise often reveals unmanaged privacy risk. For example, a vendor may host data in several regions, customer support may be provided from another country or a parent company may receive employee performance information without a clear governance structure. If management cannot answer basic location and purpose questions, transfer safeguards are likely premature.
2. Confirm the legal basis and transfer safeguards
Cross-border transfer governance starts with ordinary data protection discipline. If the organisation cannot justify the original processing activity, it will struggle to justify sending that data abroad. Boards should ask whether each major transfer has a lawful basis, a defined purpose, an appropriate notice to individuals and retention controls.
For transfers outside Jamaica, management should also show how the receiving country, vendor or group entity provides appropriate protection for the personal data. This may involve contractual safeguards, technical controls, due diligence, audit rights and documented risk assessments. The answer should be specific to the data and destination, not a generic statement that the vendor is reputable.
International guidance can help boards frame questions. The UK Information Commissioner's Office, for example, publishes practical guidance on international transfers under the UK GDPR. Jamaican organisations should not treat UK guidance as Jamaican law, but it is useful for understanding how regulators expect organisations to examine destination risk, contract terms and supplementary safeguards.
3. Test vendor controls before the contract is signed
Vendor risk is one of the most common sources of cross-border privacy risk. Boards should ask management to confirm that privacy and security due diligence happens before procurement approval, not after implementation. Once personal data has been uploaded into a system, leverage is reduced and remediation becomes more expensive.
A practical vendor review should examine the vendor's role, the data involved, hosting locations, sub-processors, security certifications, access controls, incident response commitments, retention settings, deletion support and audit rights. For high-risk vendors, a questionnaire alone may not be enough. The organisation may need a contract review, security evidence, a call with the vendor or a risk acceptance decision from senior management.
Where management needs a lean process, PLMC's guide on how to run a simple vendor privacy assessment can help teams avoid overcomplicating the first review while still capturing the evidence directors need.
4. Make security and incident response board visible
A transfer that looks acceptable on paper can still fail if security controls are weak. Boards should ask whether data is encrypted in transit and at rest, whether access is restricted by role, whether multi-factor authentication is used, whether logs are monitored and whether the vendor has tested incident response procedures.
Incident response deserves special attention because cross-border events move quickly. If an overseas processor detects unauthorised access, the Jamaican organisation may need facts within hours, not days. Contracts should require timely notice, cooperation, preservation of evidence, support with communications and clarity on who investigates what.
The board does not need operational detail in every meeting. It should receive exceptions that matter, such as overdue vendor remediation, unresolved audit findings, high-risk transfers approved outside policy, incidents involving overseas providers and repeated failure to delete or return data when contracts end.
5. Treat sensitive and high-volume data as a separate risk class
Not all transfers carry the same exposure. A mailing list sent to a regional marketing platform does not create the same risk as identity documents, health information, biometric data, criminal background checks, payroll files, customer due diligence records or transaction monitoring data shared with an overseas processor.
Boards should require management to classify transfers by risk. High-volume data, sensitive personal data, data about children, financial records and data used for profiling or automated decision-making should receive closer review. That may include a formal data protection risk assessment, stronger contract terms, stricter access controls and senior approval before the transfer begins.
This is where privacy governance connects with anti-money laundering and corporate governance. Financial institutions and regulated businesses may need to share customer due diligence data, sanctions screening outputs or suspicious transaction documentation with overseas technology providers or group compliance teams. Those arrangements should be assessed carefully so privacy safeguards do not undermine regulatory duties and regulatory duties do not become a reason to ignore privacy controls.
6. Consider GDPR and other overseas laws without losing the Jamaican anchor
Many Jamaican organisations ask whether the General Data Protection Regulation applies to them. The answer depends on the facts. GDPR may become relevant where an organisation offers goods or services to individuals in the European Union, monitors their behaviour or acts as a processor for an EU-based customer. Some contracts with international partners may also impose GDPR-style obligations even when the organisation's main legal anchor remains Jamaican law.
Boards should treat GDPR Jamaica questions as part of a wider jurisdictional analysis. The same transfer may also raise issues under UK data protection law, Canadian privacy law, US state privacy laws, Caribbean regulatory requirements or sector-specific rules. Management should be able to explain which overseas laws have been considered, which customer commitments apply and whether the organisation has accepted any contractual obligations that go beyond local statutory requirements.
The key is proportionality. A Jamaican company does not need to turn every transfer review into a global legal memorandum. It does need a repeatable method for spotting when overseas legal advice, enhanced contract review or a deeper assessment is needed.
7. Ask for board metrics, not reassurance
Boards often receive privacy updates that sound positive but do not show control. A strong cross-border privacy risk report should include trend data, exceptions and decisions required from directors. It should also distinguish between risk accepted by management and risk that requires board attention.
Useful board metrics may include:
Number of active overseas vendors processing personal data
Number of high-risk transfers and their remediation status
Percentage of vendors with current contracts and privacy clauses
Number of unapproved or legacy transfers discovered during reviews
Overdue deletion, return or retention actions after contract termination
Incidents, near misses or audit findings involving overseas processors
Training completion rates for teams that procure or manage vendors
These metrics help directors see whether the privacy programme is improving. They also support better resource decisions. If most high-risk transfers sit in one business unit or one vendor category, the board can direct management to focus attention there first.
8. Keep evidence ready for regulators, customers and partners
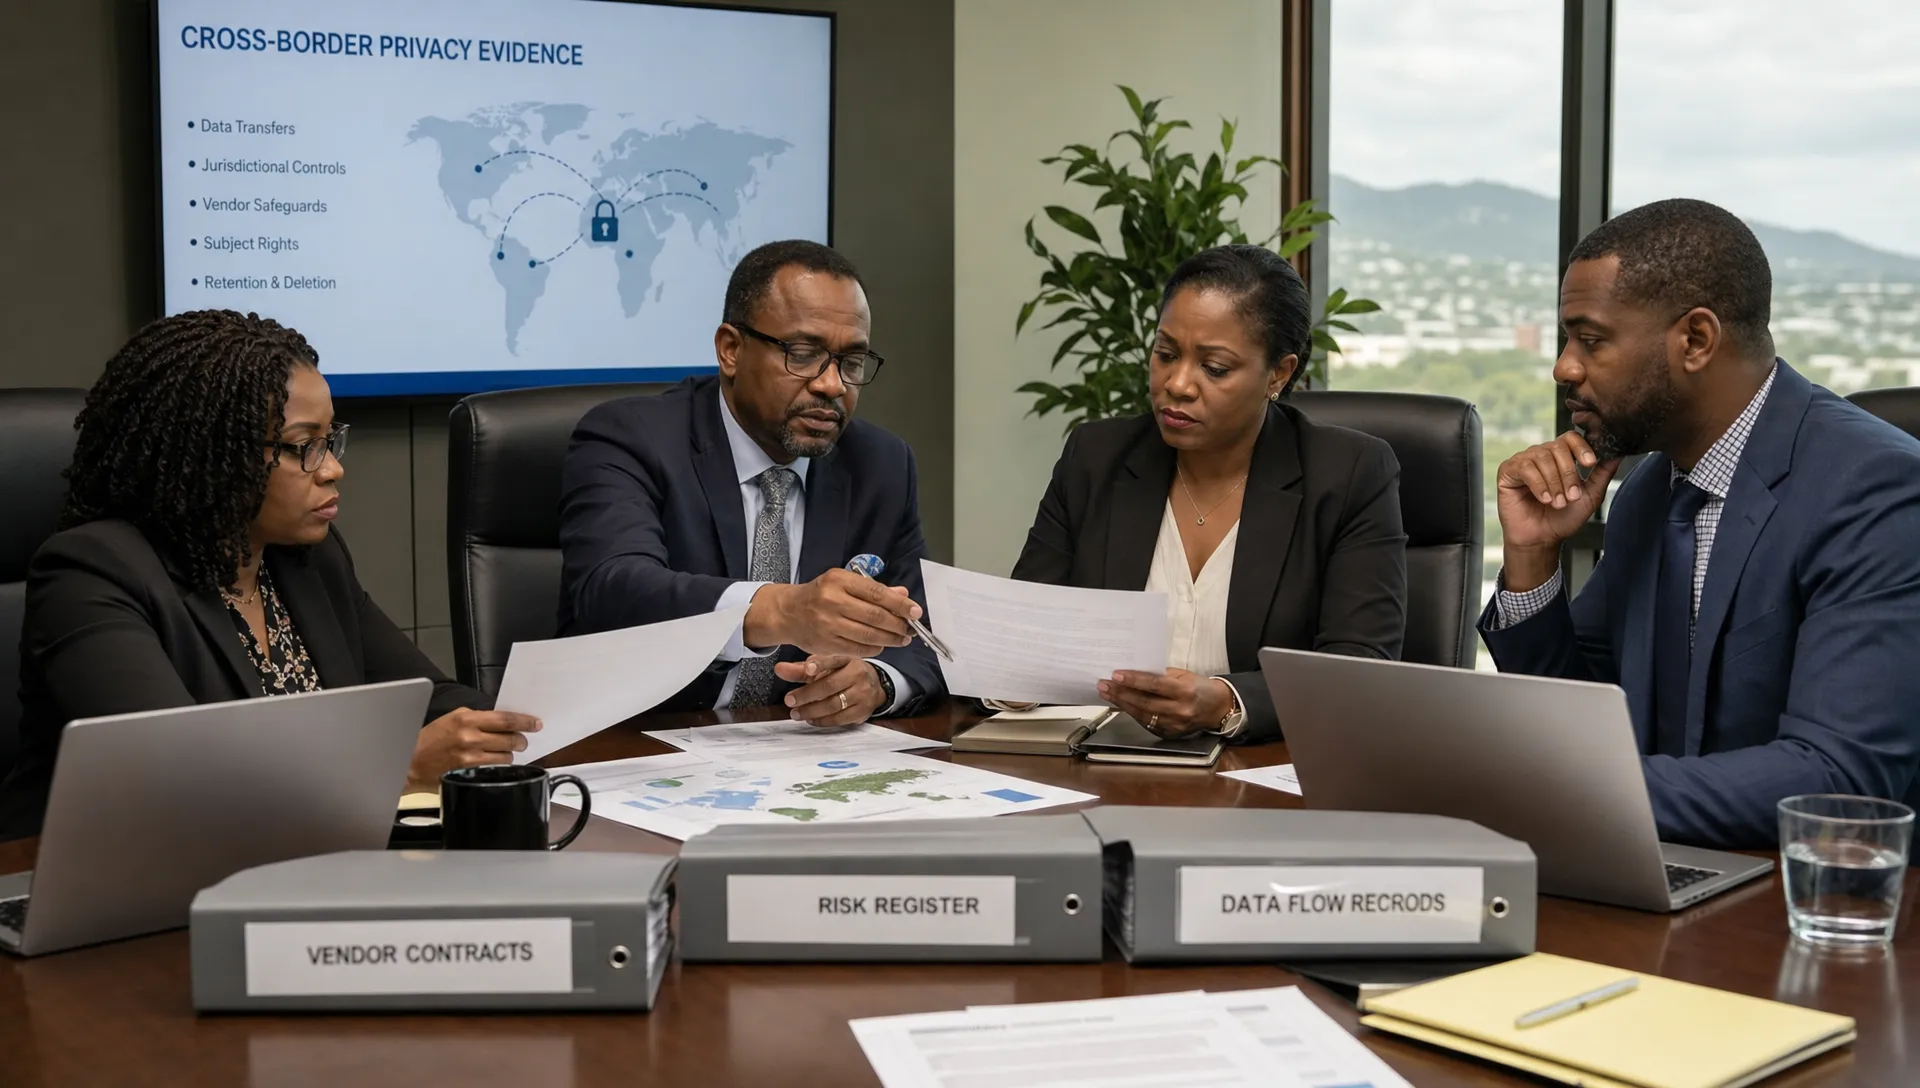
A board checklist for cross-border privacy risk is only useful if it produces evidence. In an audit, investigation or commercial negotiation, the organisation may need to show data maps, assessments, contracts, approvals, training records, vendor questionnaires, incident tests and remediation logs.
Evidence should be organised before it is requested. Customer due diligence questionnaires, cyber insurance renewals, merger activity and regulator engagement can all require fast answers. A scattered privacy file creates delay and weakens confidence, even when the underlying controls are reasonable.
For higher-risk activities, boards should ask whether a more structured assessment has been completed. PLMC's guide to data protection risk assessment scope, steps and evidence provides a useful framework for deciding what to assess, what evidence to collect and when to escalate.
How often should the board use this checklist?
The board should review cross-border privacy risk at least annually and whenever a material trigger occurs. Triggers include a new cloud platform, outsourcing arrangement, overseas affiliate sharing model, acquisition, new customer market, major vendor incident, regulatory change or transfer of sensitive data to a new jurisdiction.
For many organisations, the most practical approach is to integrate this checklist into existing board risk reporting. Management can maintain the operational register, while directors focus on material risks, exceptions, budget decisions and risk acceptance. That balance keeps the board out of day-to-day administration while preserving governance oversight.
Cross-border privacy reviews should also connect to training. Procurement, IT, HR, marketing, compliance and operations teams need to know when a tool or service creates an international transfer. If employees do not recognise the trigger, the best board policy will sit unused.
Frequently Asked Questions
What is cross-border privacy risk? Cross-border privacy risk is the legal, operational, security and reputational exposure that arises when personal data is transferred to, accessed from or processed in another country. It includes vendor risk, overseas legal requirements, incident response challenges and accountability under Jamaica's Data Protection Act, 2020.
Does the Data Protection Act, 2020 stop Jamaican organisations from using overseas cloud providers? No. The Act does not ban overseas providers, but organisations should be able to show that personal data is protected appropriately, the transfer has a lawful purpose and risks have been assessed. Contracts, security controls and documented due diligence are usually central to that evidence.
When should a board ask for a deeper assessment? A deeper assessment is sensible when the transfer involves sensitive data, large volumes of personal data, vulnerable individuals, profiling, new technology, a high-risk country, an important outsourced function or a vendor that cannot provide adequate privacy and security evidence.
Can GDPR apply to a Jamaican organisation? Yes, depending on the circumstances. GDPR may be relevant if a Jamaican organisation targets individuals in the European Union, monitors their behaviour or processes EU personal data on behalf of another organisation. Contractual obligations can also introduce GDPR-style requirements.
Who should own the cross-border transfer register? Ownership depends on the organisation, but accountability should be clear. Privacy, legal, compliance, information security, procurement and business owners usually need to contribute. The board should not maintain the register, but it should require periodic reporting on material risks and exceptions.
Need support with cross-border privacy governance?
If your board needs a clearer view of international data flows, vendor exposure or Data Protection Act, 2020 readiness, Privacy & Legal Management Consultants Ltd. can support practical privacy, data protection, cyber security, corporate governance and compliance work for Jamaican organisations.
You can explore PLMC's governance, risk and compliance support or request a free consultation through Privacy & Legal Management Consultants Ltd..