What Global Clients Expect From Your Privacy Controls
Global clients increasingly treat data protection as part of supplier quality, not as a legal footnote. If your Jamaican organisation handles customer records, employee files, payment information, health data, marketing lists or outsourced business processes for an overseas client, your privacy controls may be reviewed before pricing, service levels or technical capability are fully discussed.
That shift is practical. A client in the United States, Canada, the United Kingdom, the European Union or the Caribbean may be accountable to its own regulators, shareholders and customers for the way its vendors handle personal information. Your privacy posture can therefore influence whether you pass due diligence, win the contract, keep the contract or face tighter audit terms.
Why global clients ask tougher questions about privacy controls
International clients are not only asking whether you have a privacy policy. They want to know whether privacy is managed as an operational risk across the business. For many Jamaican firms, especially in BPO, finance, professional services, technology, education, tourism and health-adjacent services, that means privacy controls must be visible, repeatable and supported by evidence.
The expectation is also shaped by regulation. The Data Protection Act 2020 created a local compliance framework in Jamaica, but overseas clients may also need to satisfy requirements linked to GDPR, US state privacy laws, sector rules or contractual obligations. In practice, GDPR Jamaica conversations are rarely about whether the GDPR directly applies to every Jamaican business. They are more often about whether a Jamaican supplier can meet the privacy standards that a GDPR-regulated client is required to pass down.
Clients ask tougher questions because vendor risk has become board-level risk. A privacy incident at a supplier can trigger contractual claims, regulator scrutiny, reputational damage and customer notification obligations for the client. Strong privacy controls reduce that exposure and make your business easier to trust.
The baseline global clients expect from your privacy controls
The first expectation is alignment between your privacy programme and the nature of the data you handle. A small firm processing basic business contact details will not be assessed the same way as an outsourcing provider handling financial records at scale. Still, several baseline controls appear across most client reviews.
Clients usually expect named accountability. Someone must be responsible for privacy governance, escalation and decision-making. That person does not need to do everything alone, but there should be a clear owner for data protection compliance, supported by management and documented procedures.
They also expect a reliable understanding of what personal data enters the business, where it is stored, who can access it, who it is shared with and how long it is retained. Without that data inventory, policies remain generic and risk assessments become guesswork.
A further baseline is documented compliance with local law. For Jamaican organisations, that means being able to explain how your controls support Jamaica data privacy obligations under the Data Protection Act 2020, including lawful processing, transparency, security, retention, individual rights and accountability.
Evidence matters more than policy statements
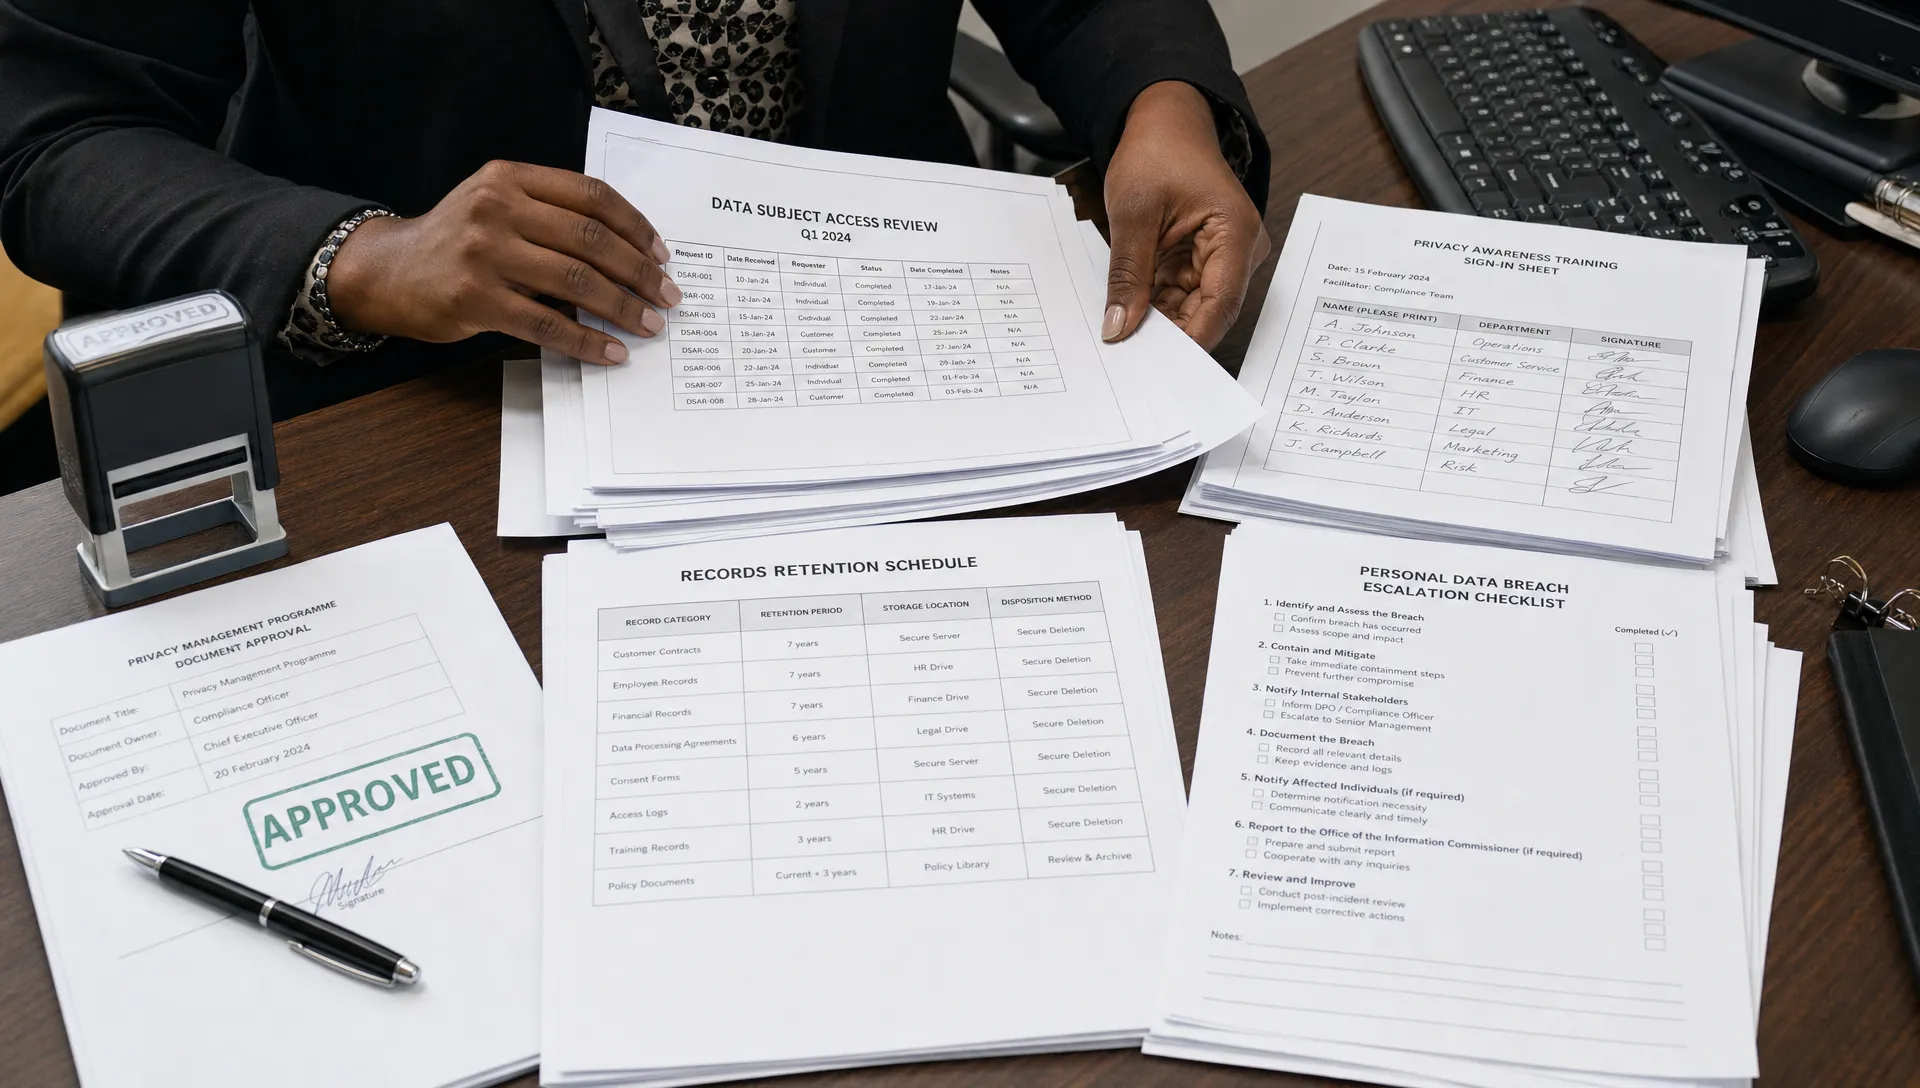
A polished policy can help, but global clients usually want proof that privacy controls work in daily operations. This is where many organisations struggle. They may have templates, but not records. They may have policies, but not training logs. They may have security tools, but not access review evidence.
If you want to understand how documentation is assessed in a compliance context, PLMC has also explained what regulators expect from privacy documentation. Client due diligence is not identical to a regulator review, but the underlying principle is similar: you need evidence that controls are active, understood and maintained.
Privacy control evidence | Why a global client asks for it | Practical example |
Data inventory or processing register | To see what data you handle and why | A record showing data categories, systems, purposes, recipients and retention periods |
Privacy notice and internal privacy policy | To confirm transparency and internal rules | Notices for customers or staff, plus staff-facing handling procedures |
Access control records | To check whether data is limited to authorised users | User access lists, role-based access rules and periodic review records |
Incident response procedure | To assess breach readiness | A documented process with reporting timelines, responsibilities and escalation contacts |
Training records | To confirm staff awareness | Attendance logs, assessment results and refresher training schedules |
Vendor register | To understand onward sharing risk | A list of processors, service providers, hosting platforms and contract status |
Retention schedule | To ensure data is not kept indefinitely | Defined retention periods and disposal methods for major data categories |
Risk assessments | To see how privacy risks are identified and reduced | DPIAs, vendor assessments or project risk reviews |
This evidence does not need to be over-engineered. It needs to be accurate, current and appropriate to the size and risk profile of the organisation.
Contract readiness for overseas client work
Contracts are where privacy expectations become enforceable. Global clients often include detailed privacy schedules or data processing clauses before work begins. These clauses may define your role, set breach notification timelines, restrict sub-processors, require security standards and give the client audit rights.
For Jamaican firms, contract readiness means understanding the difference between acting as an independent controller, a joint controller or a processor acting on client instructions. Misunderstanding the role can create tension later, especially if there is a data subject request, a deletion instruction, a regulator inquiry or a security incident.
You should also be ready to discuss cross-border transfers. A client may need to know where data will be accessed from, where systems are hosted and whether any third party outside the client’s approved jurisdictions will support the service. These questions are now standard in many procurement processes.
If your organisation regularly works with overseas clients, review PLMC’s guidance on privacy clauses for contracts with overseas clients. The stronger your contract position, the less likely you are to accept obligations your operations cannot meet.
Security controls that make privacy credible
Privacy and cyber security are not the same discipline, but clients often assess them together. A business cannot credibly promise confidentiality if access controls are weak, devices are unmanaged or incidents are handled informally.
Common security controls that support privacy include multi-factor authentication, strong password rules, encryption where appropriate, secure backups, patch management, logging, malware protection, remote access controls and role-based permissions. Clients may also ask whether you follow recognised frameworks such as the NIST Cybersecurity Framework, particularly if you process sensitive or high-volume data.
The key is not to claim a framework you do not actually operate. A measured answer is better than an inflated one. If you are still maturing, explain the controls already in place, the gaps identified and the improvement plan approved by management.
Operational controls clients look for after onboarding
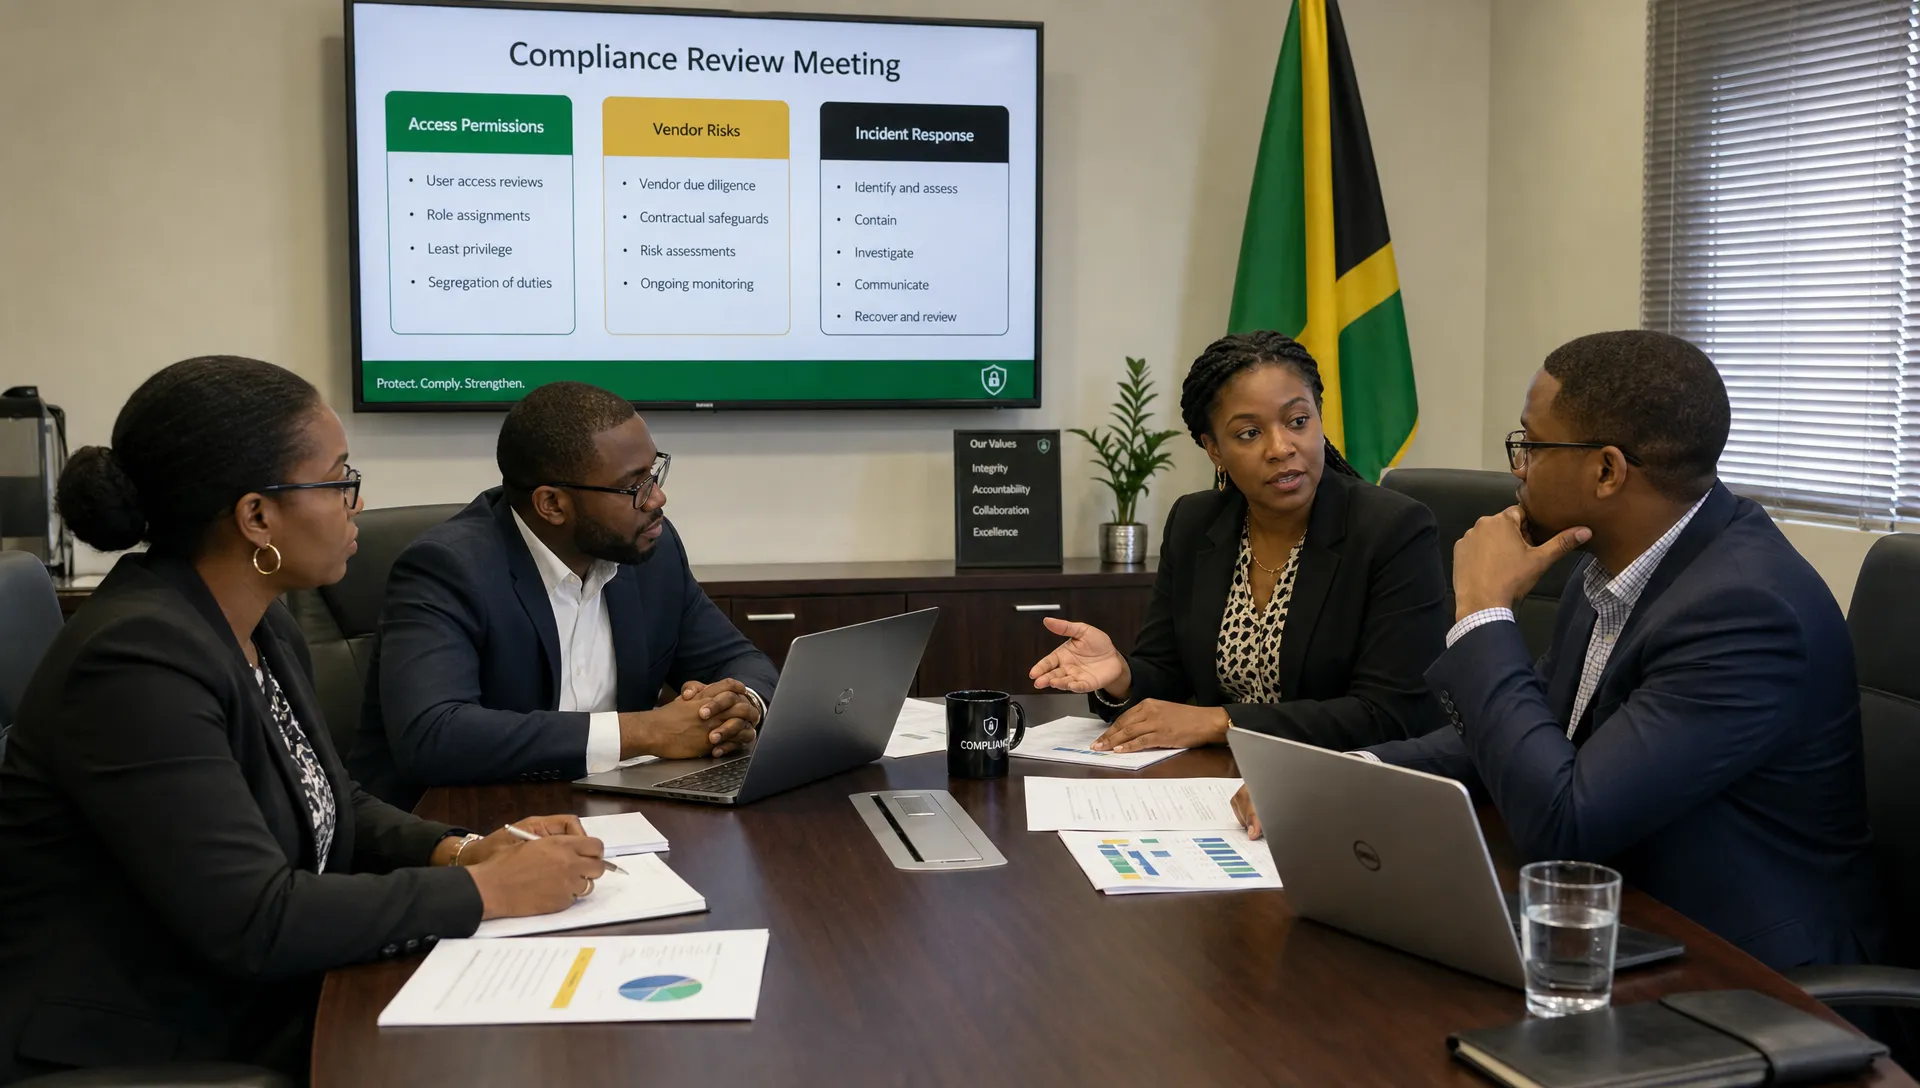
Client scrutiny does not end when the contract is signed. Many global clients now conduct periodic reviews, request attestations or require evidence after major changes. This means privacy controls must be embedded into workflows rather than stored in a folder for occasional review.
Operationally, clients expect data minimisation. Staff should collect only what is needed for the agreed purpose, avoid informal copies and limit unnecessary exports. If a spreadsheet containing personal data is emailed widely because it is convenient, the policy has not translated into practice.
Clients also expect clear rules for retention and deletion. If the contract ends, they may require return or deletion of data within a defined period. Your organisation should know which systems hold the client’s data, including backups, shared drives, email attachments and third-party platforms.
Individual rights processes matter as well. Even where the overseas client manages direct communication with individuals, your organisation may need to support access, correction, deletion or restriction requests within tight timeframes. A simple internal workflow can prevent delays and confusion.
Training and culture are part of the control environment
Global clients know that many privacy failures begin with ordinary human behaviour: sending files to the wrong recipient, using personal email, discussing client information in public areas or storing documents in unmanaged locations. That is why data privacy training Jamaica programmes are increasingly relevant for organisations that want to compete for international work.
Training should be specific to job roles. Customer support teams need rules for identity verification and call notes. HR teams need guidance on employee records. IT teams need escalation steps for suspicious access. Finance and compliance teams may need additional controls where privacy overlaps with fraud prevention, sanctions screening or anti-money laundering obligations.
Culture also matters because clients can sense when privacy is performative. If staff cannot explain basic handling rules, or if managers bypass controls to save time, the organisation appears risky. PLMC’s article on building a privacy culture people follow is useful for organisations that want policies to move beyond paper compliance.
How privacy links with corporate governance and risk management
Privacy controls should not sit apart from corporate governance. Global clients increasingly expect privacy to be reported through the same governance channels as other material risks. That may include senior management updates, board reporting, risk registers, internal audits and documented decisions on high-risk processing.
This is especially important where privacy intersects with regulated activities. For example, anti-money laundering processes may require identity verification, transaction monitoring and record retention. Those activities can be lawful and necessary, but they still need privacy controls around access, purpose limitation, security and retention.
A mature governance approach connects privacy, cyber security, compliance, legal review, vendor management and business continuity. That integrated view helps leadership understand trade-offs and allocate resources where risk is highest.
How to prepare for global client due diligence
Preparation should begin before the client sends a questionnaire. If you wait until procurement asks for evidence, you may rush responses, overpromise or discover that key records are missing.
Start with a focused readiness review. Identify the services you provide to overseas clients, the personal data involved, the systems used and the contractual obligations already accepted. Then compare your current controls against the questions clients usually ask.
A practical due diligence pack can include:
A short privacy governance summary naming responsible roles and escalation paths
A current data inventory for major services or client processes
Copies of relevant privacy, security, retention and incident response policies
Training evidence for staff who handle client data
Vendor and sub-processor details, including hosting locations where known
Recent access review records for systems containing personal data
A breach response summary with notification and escalation steps
A remediation tracker showing open gaps, owners and target dates
The remediation tracker is often underrated. Clients do not expect every supplier to be perfect, but they do expect honesty and control. A documented improvement plan can be more credible than vague assurances that everything is already handled.
Common gaps that concern global clients
Certain weaknesses raise concern quickly during international due diligence. One is uncertainty about where data is stored. If a supplier cannot identify systems, cloud platforms or third-party tools used in delivery, the client may see that as a sign of unmanaged risk.
Another common gap is weak incident escalation. A staff member may know something went wrong, but not know who to notify or how quickly to act. For overseas clients with strict notification duties, delay can be a serious contractual issue.
Generic policies also create concern. A policy copied from another jurisdiction, filled with broad promises and not matched to Jamaican operations will not satisfy a careful client. The document should reflect what your organisation actually does, including local legal requirements, service delivery methods and realistic controls.
Finally, clients notice when privacy is treated only as a legal department issue. Strong data protection compliance needs cooperation across operations, IT, HR, finance, procurement, compliance and leadership.
Turning privacy controls into a competitive advantage
Strong privacy controls can shorten procurement cycles, reduce contract friction and position a Jamaican organisation as a safer partner for international work. They also support resilience. When staff know the rules, systems are controlled and evidence is ready, your business can respond faster to client questions, audits and incidents.
This is not only a compliance exercise. It is a trust signal. Global clients want suppliers that understand the value of personal information and can protect it without slowing down the business unnecessarily.
For Jamaican organisations, the opportunity is clear. By aligning local Data Protection Act 2020 obligations with global client expectations, you can move from reactive compliance to confident participation in international markets.
Frequently Asked Questions
Do global clients expect Jamaican businesses to comply with GDPR? Not always directly. However, if a Jamaican business handles personal data for a client subject to GDPR, the client may require GDPR-style contractual, security and accountability controls.
What is the most important privacy document for client due diligence? There is no single document that answers every concern. A data inventory, privacy policy, incident response procedure, training records and vendor register usually work together to show control.
How does the Data Protection Act 2020 affect overseas client work? It gives Jamaican organisations a local privacy compliance foundation. Overseas clients often want to see that your handling of personal data is lawful, transparent, secure and supported by accountability measures.
Should privacy controls be reviewed before signing an international contract? Yes. Reviewing controls before signing helps you avoid accepting breach timelines, audit rights, deletion duties or sub-processor restrictions that your organisation cannot meet.
Can PLMC help prepare an organisation for privacy due diligence? Privacy & Legal Management Consultants Ltd. supports organisations in Jamaica with data privacy, protection and compliance solutions, including implementation, training, governance and risk-focused support.
Strengthen your privacy controls before clients ask
If your organisation works with global clients, privacy readiness should be part of business development, procurement and governance planning. A client questionnaire should not be the first time you discover gaps in your controls.
Privacy & Legal Management Consultants Ltd. helps Jamaican organisations approach privacy, compliance and governance in a practical way. To review your current position, identify priority gaps or prepare for overseas client due diligence, start with the resources and support available through Privacy & Legal Management Consultants Ltd..