

International Privacy Compliance for Financial Services
Financial institutions rarely operate within one legal border, even when their branches, staff and customers are mainly in Jamaica. Card networks, cloud platforms, correspondent banks, overseas clients, fintech partners and regulators all create privacy touchpoints. That is why international privacy compliance for financial services needs more than a local policy template. It requires a risk based framework that connects Jamaica's Data Protection Act, cross-border transfer controls, anti-money laundering obligations, cybersecurity and contract governance.
For banks, credit unions, remittance providers, insurers, investment firms, payment processors and fintech companies, privacy risk is also business risk. A weak control in customer onboarding can affect AML compliance. A vague outsourcing contract can slow breach response. A poorly mapped data flow can cause problems when serving customers in the European Union, United Kingdom, Canada or the United States.
Why international privacy compliance for financial services is different
Financial services organisations process unusually sensitive information. A routine customer file may include identification documents, taxpayer details, biometric data, source of funds information, transaction histories, account balances, geolocation data, beneficiary records and risk ratings.
That information is valuable to criminals and heavily scrutinised by regulators. It also moves constantly. A payment transaction may involve a Jamaican institution, a card scheme, an overseas processor, a fraud monitoring tool and a correspondent bank. A digital banking app may rely on cloud hosting, analytics providers, authentication vendors and support teams in more than one country.
International privacy compliance for financial services must therefore answer three questions at the same time:
Which laws apply to each customer, product and market?
Where does personal data move, including through vendors and group companies?
Which controls prove that the institution is using, sharing, retaining and securing data lawfully?
This is not only a legal exercise. It sits at the centre of governance, risk and compliance because the same data supports onboarding, transaction monitoring, sanctions screening, fraud prevention, complaints handling and regulatory reporting.
Start with Jamaica's Data Protection Act 2020
For Jamaican financial institutions, the baseline is the Data Protection Act, 2020 and guidance from Jamaica's Office of the Information Commissioner. The Act establishes core standards for processing personal data, including fairness, transparency, purpose limitation, data minimisation, accuracy, security, retention limits and respect for individual rights.
The practical point is simple: overseas requirements should not be treated as a separate privacy project. They should be layered onto the local data protection compliance programme. If the organisation cannot explain what personal data it holds under Jamaica's framework, it will struggle to satisfy GDPR, UK GDPR, Canadian, US or contractual client requirements.
What financial institutions should document first
Before comparing international laws, document the local processing picture. This should include customer onboarding, account servicing, payment processing, lending, insurance underwriting, investment advice, collections, fraud monitoring, AML reviews, marketing and complaints.
A useful record should identify the data categories, purpose, lawful basis or processing condition, system owner, retention period, data recipients, transfer countries and security controls. It should also distinguish between ordinary personal data and higher risk information such as government identifiers, financial history, health information, biometrics and criminal or regulatory screening results.
Good documentation does more than satisfy auditors. It gives compliance, legal, cybersecurity, operations and business teams one shared view of risk. That shared view is essential when a new fintech partnership, overseas product launch or cloud migration is proposed.
Map cross-border data flows before assessing foreign laws
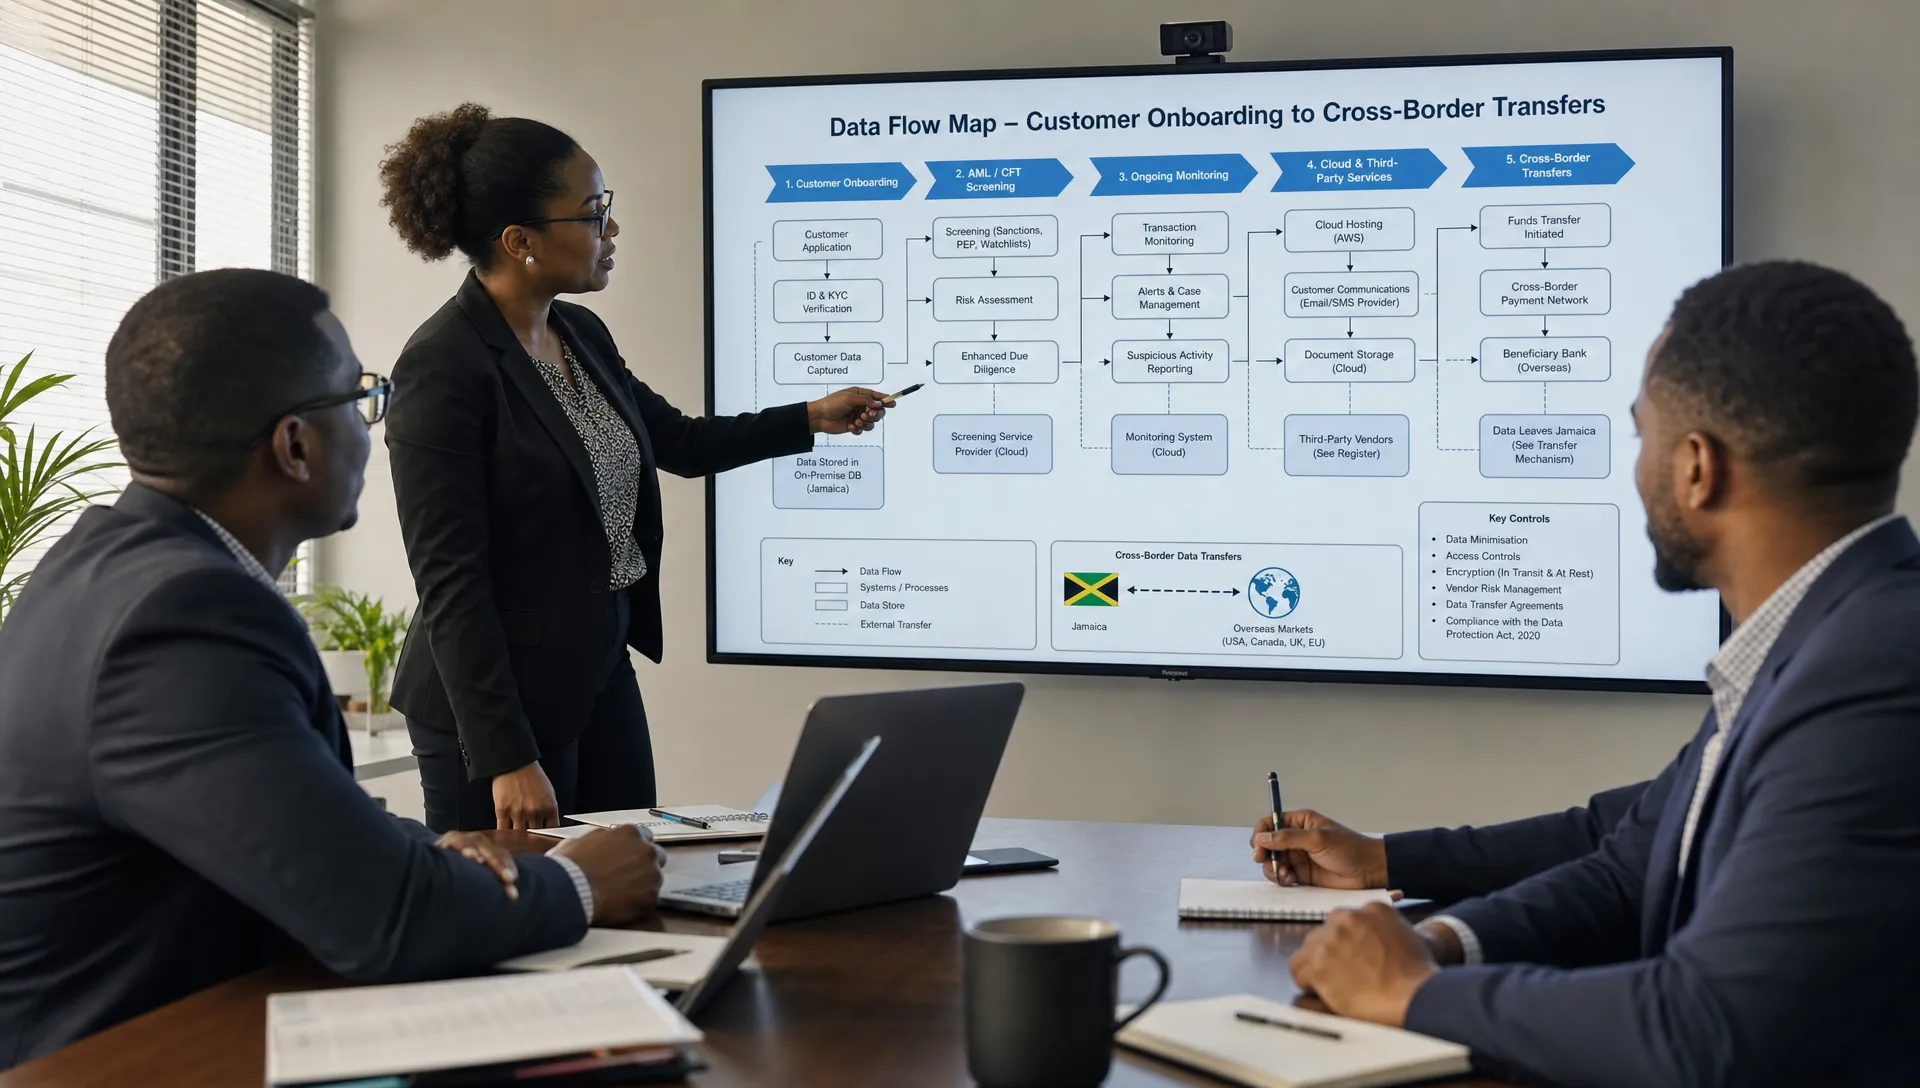
Many privacy failures begin with an incomplete data map. Senior management may know the main core banking provider, but not every analytics plug-in, support desk, identity verification tool, cloud backup, credit scoring service or group reporting pathway.
International privacy compliance for financial services depends on knowing where data actually travels. This includes active transfers, such as sending customer files to an overseas processor, and indirect transfers, such as allowing a foreign support team to access a Jamaican database.
Financial process | Common personal data involved | Cross-border risk | Control to prioritise |
Customer onboarding | IDs, proof of address, tax details, source of funds | Overseas identity verification or screening vendors | Vendor due diligence and transfer terms |
Card and digital payments | Transaction data, device data, merchant data | Card networks, processors and fraud tools outside Jamaica | Security standards and processor contracts |
Wealth and investment services | Portfolio details, risk profiles, beneficiaries | Group reporting or foreign custodian relationships | Role mapping and purpose limitation |
AML monitoring | KYC files, sanctions results, suspicious activity indicators | Screening databases and correspondent banking requests | Access controls, retention rules and legal review |
Customer support | Contact details, account queries, recordings | Remote support teams or global ticketing tools | Training, access logging and data minimisation |
If your institution is unsure which foreign rules may be triggered, a structured review of when overseas data laws apply to Jamaican companies can help identify exposure before it becomes a contract or regulatory issue.
When GDPR, UK and US privacy rules may matter
The EU General Data Protection Regulation is often the first overseas law Jamaican firms ask about. The European Commission's data protection overview explains the GDPR framework, but the key question for a Jamaican financial institution is whether its activities connect sufficiently to people in the EU.
A GDPR Jamaica assessment may be needed where a Jamaican firm offers services to EU residents, monitors behaviour of EU users, processes data for an EU regulated client or receives EU personal data under a contract. Similar analysis may be needed for UK GDPR where UK individuals or clients are involved.
US privacy rules require a different approach because the United States does not have one single federal privacy law equivalent to the GDPR. Instead, financial institutions may encounter sector rules, state privacy laws, Federal Trade Commission enforcement expectations, breach notification laws and contractual obligations from US clients or partners. Jamaican firms serving US clients should pay close attention to the specific state, sector and business relationship involved.
International privacy compliance for financial services should not become a checklist of every foreign law in the world. The better approach is to identify triggers, prioritise the laws most likely to apply and create controls that can be adapted across jurisdictions.
Build one control framework, not separate privacy silos
Financial services firms often manage privacy, AML, cybersecurity, outsourcing and operational risk through different teams. That separation is understandable, but it can create gaps. A privacy policy may say customer data is retained only as long as necessary, while AML procedures require records to be kept for regulatory purposes. A cybersecurity team may approve a vendor's technical controls, while legal has not reviewed transfer restrictions.
A unified framework reduces duplication and makes testing easier. It should connect board oversight, policies, risk assessments, contracts, staff training, incident response and ongoing monitoring.
Control area | What good looks like | Evidence to keep |
Governance | Clear ownership for privacy, security, AML and outsourcing risks | Board minutes, committee reports, role descriptions |
Data inventory | Current records of processing and cross-border transfers | Data maps, system registers, vendor lists |
Lawful processing | Documented purpose and basis for each major activity | Privacy notices, DPIAs, legal assessments |
Vendor management | Due diligence before onboarding and periodic reviews | Contracts, risk ratings, audit reports |
Security | Controls matched to data sensitivity and threat level | Access logs, policies, test results, incident records |
Training | Role based privacy and data handling instruction | Attendance records, materials, completion reports |
Monitoring | Regular testing of controls and issue remediation | Internal audit findings, action trackers, management reports |
This kind of integrated framework also helps global partners trust the institution. Many overseas clients and banks want assurance that privacy obligations are embedded in governance rather than treated as a one-time document exercise.
Where AML and privacy obligations intersect
Financial institutions must collect enough information to understand customers, detect suspicious activity and meet legal obligations. At the same time, privacy law expects personal data to be adequate, relevant and limited to what is needed for a stated purpose.
That tension is manageable when the institution clearly documents why it collects each category of information. KYC documents, sanctions results, politically exposed person checks and transaction monitoring alerts should be tied to defined AML, fraud prevention or regulatory purposes. Access should be limited to staff who need the information, and retention should reflect legal obligations rather than convenience.
The Financial Action Task Force Recommendations set global expectations for AML and counter terrorist financing controls. Financial institutions in Jamaica must translate those expectations into local procedures while still respecting data protection principles.
The overlap can be complex, especially when handling suspicious activity, enhanced due diligence or information requests from foreign correspondent banks. PLMC has explored this operational tension in more detail in its article on how AML and data privacy rules intersect in practice.
Contracts and outsourcing need special attention
Outsourcing is a major source of privacy risk in financial services. Cloud hosting, payment processing, customer relationship management, e-signature tools, call centres, screening databases and software support can all involve personal data.
International privacy compliance for financial services requires contracts that identify the parties' roles and responsibilities. Is the vendor a processor, independent controller, joint controller or service provider under a specific overseas law? Can the vendor use subcontractors? Where will data be stored or accessed? What happens if the vendor receives a government request or suffers a breach?
Strong contracts usually address confidentiality, security, approved purposes, audit rights, breach notification, cross-border transfers, subcontracting, return or deletion of data and assistance with data subject rights. For overseas clients, privacy clauses also need to align with the client's jurisdiction and risk appetite. Jamaican organisations negotiating international agreements may benefit from reviewing practical guidance on privacy clauses for contracts with overseas clients.
Payment data deserves additional care. If an institution stores, processes or transmits cardholder data, the PCI Security Standards Council framework may be relevant alongside privacy and cybersecurity requirements. PCI compliance does not replace data protection compliance, but it can support the security controls expected for payment environments.
Breach response must work across jurisdictions
A cyber incident at a financial institution can quickly become a multi-jurisdictional privacy event. One ransomware attack or misdirected data file may affect Jamaican customers, foreign customers, overseas vendors and regulated clients.
The response plan should define how incidents are detected, escalated, assessed, contained, investigated and reported. It should also identify who decides whether individuals, regulators, clients, insurers, law enforcement or contractual counterparties must be notified.
Different laws and contracts may impose different notification thresholds and timelines. For example, the EU GDPR uses a 72 hour supervisory authority notification requirement in certain personal data breach cases. Other jurisdictions and contracts may use different standards. The safest approach is to maintain an incident matrix that maps likely notification duties by jurisdiction, client and data type.
Financial institutions should also test their breach plans through tabletop exercises. These exercises reveal practical issues, such as incomplete vendor contacts, unclear decision rights, weak evidence preservation or uncertainty about customer communications.
A practical roadmap for Jamaican financial institutions
International privacy compliance for financial services is easier to manage when the organisation treats it as a phased programme rather than a single legal review. The following roadmap works for established institutions and growing fintechs.
Confirm governance ownership: Assign responsibility across privacy, legal, compliance, AML, cybersecurity, operations and senior management so that no material data risk sits between departments.
Update the data inventory: Map systems, vendors, countries, data categories, retention periods and access rights for major financial processes.
Identify applicable overseas laws: Review customer locations, marketing activity, contracts, group relationships, processors and regulatory commitments to determine which foreign regimes matter.
Strengthen vendor controls: Reassess high risk vendors, review contracts and verify that security, transfer, breach and subcontracting terms match the data risk.
Align AML and privacy procedures: Document the reason for KYC and monitoring data, limit access and maintain retention rules that reflect legal duties.
Train role specific teams: Give frontline staff, AML analysts, IT teams, relationship managers and executives training that matches the data decisions they make.
Test and improve: Conduct audits, tabletop exercises and periodic reviews so that the framework remains accurate as products, markets and vendors change.
This roadmap also supports board reporting. Senior leaders should be able to see the institution's highest privacy risks, what is being done about them and whether remediation is progressing.
What boards and executives should ask
Board members do not need to manage every privacy control, but they should ask clear questions. Which data flows are most sensitive? Which overseas laws affect the institution's strategy? Which vendors would create the greatest disruption if they failed? How quickly could the institution assess a cross-border breach? Are AML, cybersecurity and privacy teams using the same risk picture?
These questions make privacy measurable. They also help ensure that international growth, digital transformation and outsourcing decisions are made with a realistic view of legal and operational exposure.
Frequently Asked Questions
Does Jamaica's Data Protection Act apply if a financial institution also follows GDPR? Yes. A Jamaican financial institution should treat the Data Protection Act, 2020 as a local baseline. GDPR or other overseas rules may add obligations where there is a relevant connection to foreign individuals, clients or markets.
When should a Jamaican financial services firm conduct a GDPR assessment? A GDPR assessment is useful when the firm offers services to EU residents, monitors EU users, processes personal data for an EU client or receives EU personal data under a contract.
Can AML obligations override privacy requirements? AML laws may require institutions to collect and retain certain information, but that does not remove privacy duties. The institution should document the legal purpose, restrict access, protect the data and avoid collecting information that is not needed.
What is the biggest privacy risk in outsourcing financial services operations? The biggest risk is often loss of control over where data goes, who can access it and how quickly the vendor will respond during an incident. Contracts, due diligence and monitoring are essential.
How often should financial institutions review international privacy controls? Reviews should occur at least periodically and whenever there is a major change, such as a new overseas market, cloud migration, fintech partnership, product launch or regulatory requirement.
Strengthen privacy compliance before it becomes a regulatory issue
International privacy compliance for financial services is no longer a niche concern for multinational banks. It affects Jamaican financial institutions that use overseas vendors, serve foreign clients, process cross-border payments or participate in global financial networks.
Privacy & Legal Management Consultants Ltd. supports organisations in Jamaica with data protection implementation, corporate governance, AML compliance, cybersecurity alignment, GRC integration, training and privacy awareness. If your institution needs to assess its current privacy posture or prepare for cross-border obligations, a structured consultation can help you move from uncertainty to an actionable compliance plan.