

How to Choose a Lead Privacy Law for Global Operations
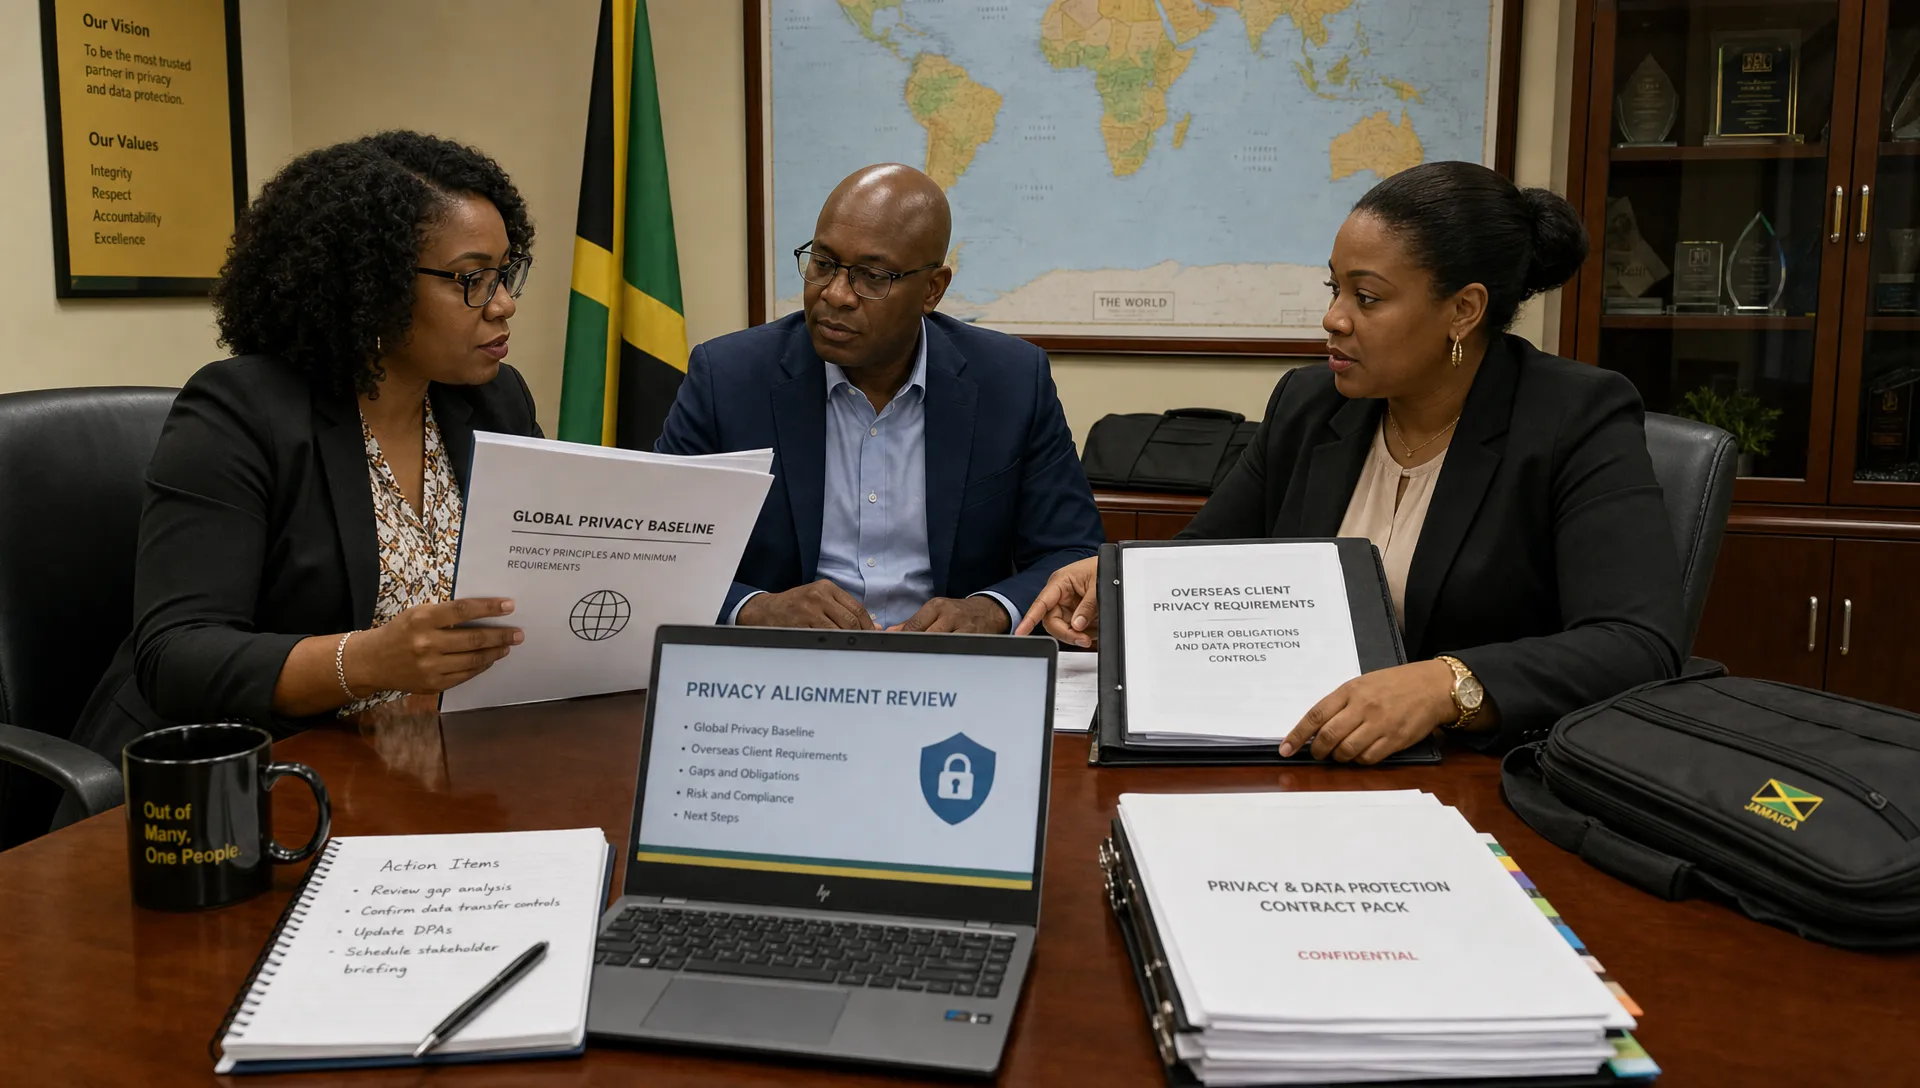
Global expansion makes privacy governance harder because every market brings its own rules, regulator expectations, contract language and customer assumptions. Choosing a lead privacy law gives your organisation one practical baseline for data protection decisions, so teams do not rebuild policies from scratch every time a Jamaican business serves a new market, launches a new platform or signs an overseas client.
A lead law is not a shortcut around local compliance. It is an internal anchor. You still have to assess the laws that apply in each country, but the lead law sets the default standard for notices, contracts, privacy impact assessments, breach response, vendor due diligence and staff training.
For Jamaican organisations, the decision often sits between Jamaica's Data Protection Act, 2020, the EU GDPR, the UK GDPR, US privacy rules and customer-specific requirements. The right choice depends on where the organisation is established, whose personal data it handles, where its clients operate and how much privacy maturity the business can realistically maintain.
What a lead privacy law does, and what it cannot do
A lead privacy law is the primary framework your organisation uses to design global privacy controls. It answers questions such as: what should our standard privacy notice contain, when should we run a privacy impact assessment, what clauses should be in processor contracts and how do we handle data subject rights across jurisdictions?
It does not decide whether a foreign law applies. That question depends on territorial scope, establishment, targeting, monitoring, contractual promises, sector rules and local regulator guidance. If your organisation processes personal data about EU individuals in a way that triggers the EU GDPR, adopting Jamaica's law as your baseline will not remove GDPR obligations.
It also does not replace governing law clauses in commercial contracts. A services agreement may be governed by Jamaican law, New York law or English law, but privacy obligations can still arise from another jurisdiction because of the data being processed.
A lead law works best when it is treated as the compliance floor, then adapted with local overlays.
Why Jamaican organisations need a global privacy baseline
Jamaican organisations increasingly process data across borders through cloud services, outsourcing, tourism platforms, financial services, call centres, professional services and software tools. Even a local company can become internationally exposed if it uses overseas vendors, serves foreign customers or handles employee data in global HR systems.
Jamaica's Data Protection Act, 2020 gives local organisations a strong domestic foundation. The Office of the Information Commissioner is the key authority for Jamaica's data protection regime, and Jamaican businesses should treat local compliance as non-negotiable.
The challenge is that global clients may ask for more than local compliance. They may request GDPR-style contract clauses, security questionnaires, breach notification timelines, evidence of data privacy training or proof that cross-border transfers are governed properly. If your internal programme has no chosen baseline, every client request becomes a one-off negotiation.
Before selecting a global baseline, it is useful to assess overseas obligations by market, data type and processing activity. PLMC has a separate guide on how Jamaican organisations can assess overseas privacy laws before expansion, which is a useful companion to this lead-law decision.
Criteria for choosing a lead privacy law
The best lead law is not always the strictest law. It is the law that gives your organisation the most reliable, usable and commercially credible baseline for its actual risk profile.
Start with territorial reach. If most of your international exposure involves EU or UK clients, the GDPR or UK GDPR may be a natural baseline. If the organisation mainly operates in Jamaica and processes Jamaican customer or employee data, Jamaica's Data Protection Act, 2020 should remain central even if overseas overlays are added.
Then consider customer expectations. A business that sells to multinational companies may face privacy due diligence based on GDPR concepts even where GDPR does not directly apply. The phrase "GDPR Jamaica" often appears in client conversations because overseas buyers want to know whether a Jamaican provider can meet global privacy standards.
Operational fit matters as well. A privacy law that looks excellent on paper can fail if teams cannot implement it. The lead law should map cleanly to your current governance structure, technology environment, reporting lines, vendor management process and training capacity.
Finally, weigh enforcement and contract pressure. A low-risk local activity may justify a Jamaica-first baseline with targeted foreign overlays. A cross-border technology or outsourcing operation may need a more stringent baseline from day one.
Comparing common candidate laws
The table below is not a substitute for legal advice, but it helps frame the decision. Many organisations will choose one baseline and then maintain a register of local variations.
Candidate framework | When it can work as the baseline | Main watch point | Practical fit for Jamaican organisations |
Jamaica Data Protection Act, 2020 | The organisation is established in Jamaica and mainly handles Jamaican personal data | Overseas clients may still require GDPR, UK or US privacy controls | Essential domestic foundation for Jamaican controllers and processors |
EU GDPR | The organisation targets EU individuals, monitors EU behaviour or works with EU clients | It can create obligations that exceed what some low-risk operations need | Strong global benchmark for mature cross-border programmes |
UK GDPR and UK Data Protection Act 2018 | The organisation serves UK clients or receives UK personal data | Similar to GDPR, but separate from the EU regime | Useful for Jamaican firms with UK business relationships |
US state and sector privacy rules | The organisation serves US customers or handles regulated US data | The US has no single comprehensive federal privacy law | Better as an overlay unless the US is the dominant market |
Canada PIPEDA, Brazil LGPD or other national laws | The organisation has a clear market-specific exposure | Each law has its own scope, rights and regulator expectations | Best used as local overlays unless that market drives the business |
This comparison shows why there is rarely a universal answer. A lead law should reduce complexity, not hide it.
How to choose a lead privacy law for global operations
To choose a lead privacy law for global operations, use a structured process rather than defaulting to the law that sounds most familiar. The following sequence works well for boards, legal teams, compliance teams and data protection leads.
Map your data footprint: Identify where personal data comes from, where it is stored, who accesses it, which vendors process it and which countries are involved.
List laws that may apply: Include local law, customer-country law, vendor-country law, sector rules and contractual requirements.
Rank exposure by risk and revenue: Give more weight to markets that generate significant revenue, involve sensitive data or create regulator exposure.
Compare control requirements: Look at lawful basis, transparency, consent, individual rights, breach response, transfers, vendor controls and accountability.
Select the most useful baseline: Choose the law that covers the largest share of your actual obligations while remaining operationally sustainable.
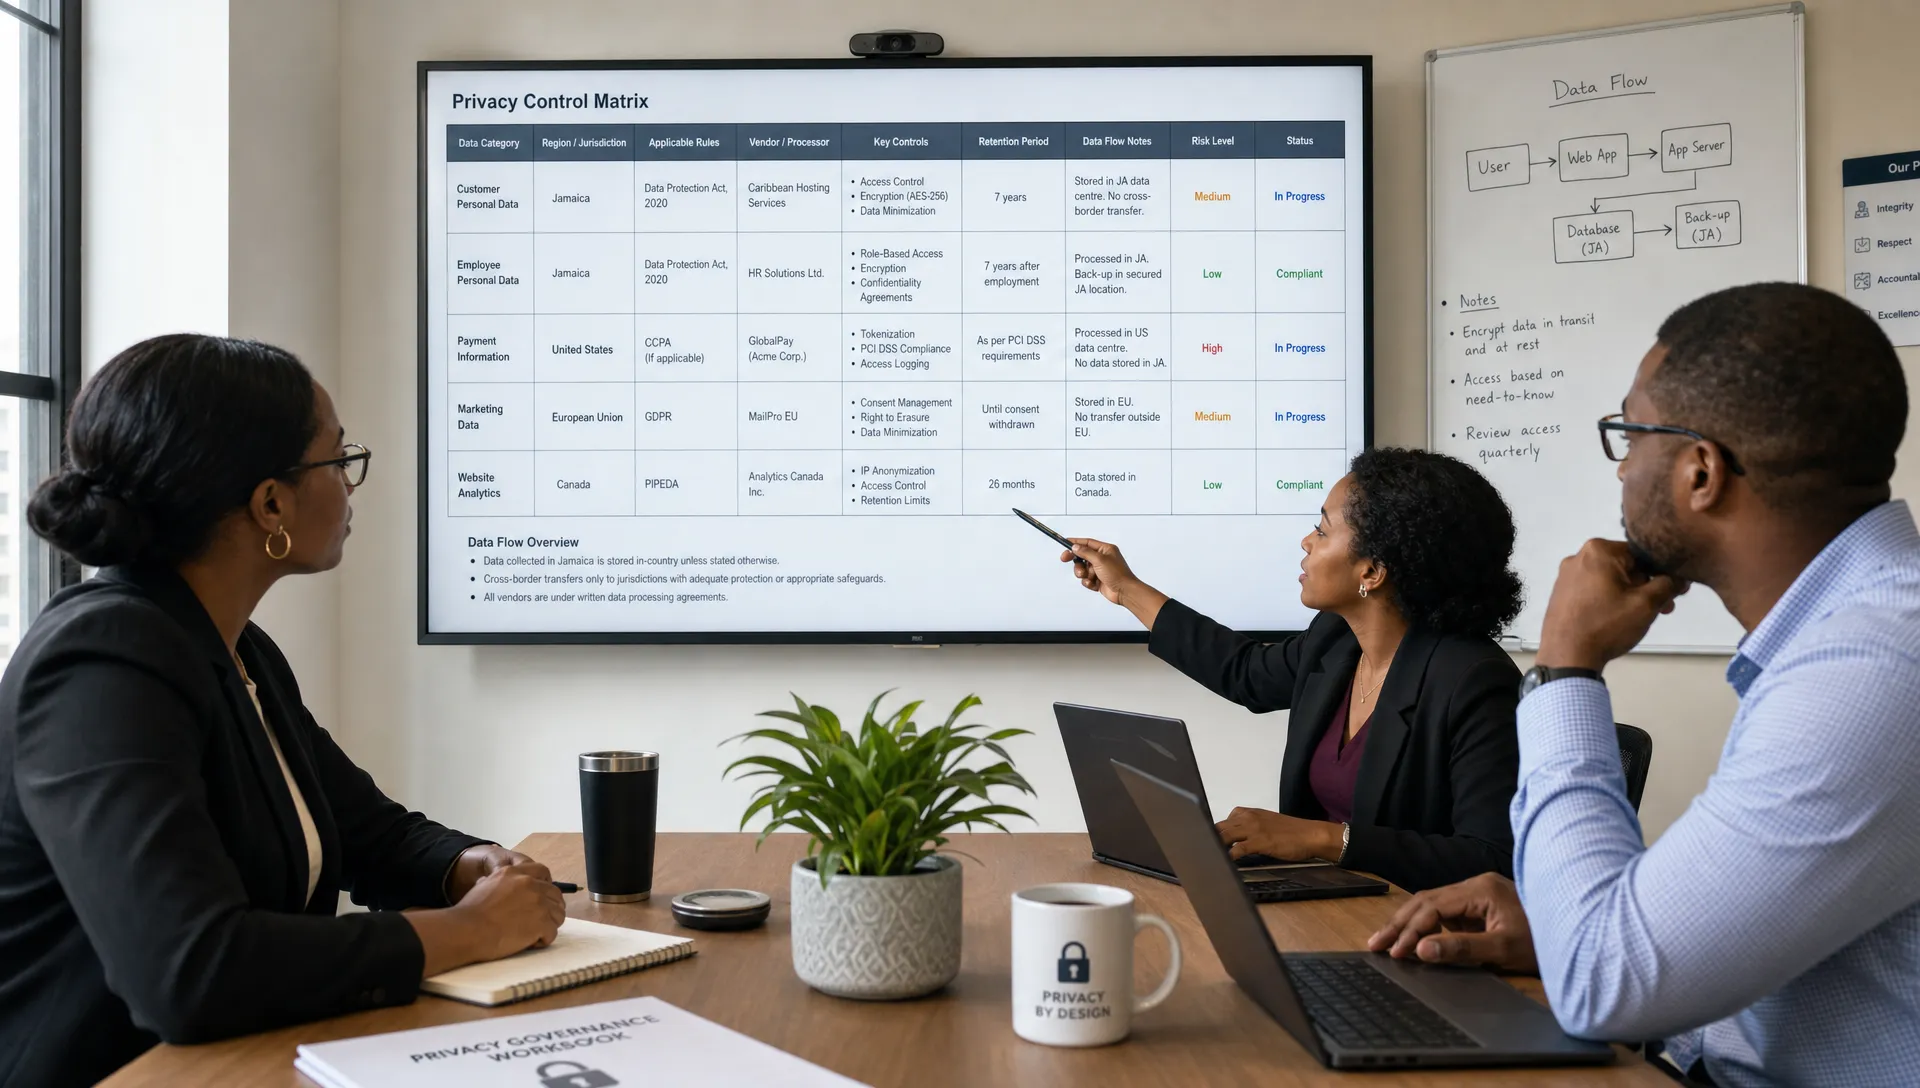
Document local overlays: Keep a living matrix that shows where a country, sector or client requires more than the baseline.
The decision should be approved at a governance level, not left to one department. Privacy affects legal risk, technology design, customer trust, procurement, human resources, marketing and cyber security.
Avoid the "highest standard" trap
Many organisations assume the safest answer is to use the strictest law everywhere. That can be sensible in some cases, especially where GDPR exposure is real and privacy maturity is high. It can also waste resources if controls are copied without understanding the business context.
For example, a Jamaican organisation may adopt GDPR concepts for transparency, accountability, processor contracts and data subject rights. That does not mean the organisation can ignore local requirements under Jamaica's Data Protection Act, 2020. Domestic registration, regulator engagement, local notices, employment practices and sector obligations still need attention.
The same point applies to regulated sectors. A financial institution cannot choose a privacy baseline and overlook anti-money laundering recordkeeping, customer due diligence, fraud monitoring or cyber security expectations. Privacy has to sit inside the wider governance, risk and compliance model.
A better approach is to choose a high-quality baseline, then add local, sector and contractual requirements where they are stricter or different.
Build a control matrix from the chosen baseline
Once the lead law is chosen, translate it into a practical control matrix. This is where strategy becomes daily compliance.
Control area | Baseline question | Local overlay question |
Privacy notices | What must individuals be told before or during collection? | Does any country require specific wording, timing or language? |
Lawful basis or legal condition | What makes the processing lawful? | Does local law treat consent, contract, legal obligation or legitimate interests differently? |
Individual rights | Which rights will be honoured as standard? | Are response times, exceptions or identity checks different in a specific market? |
Vendor contracts | What clauses apply to processors and service providers? | Are transfer clauses, audit rights or subcontracting rules stricter in the client country? |
Cross-border transfers | What transfer mechanism is required? | Are there localisation, adequacy or regulator approval requirements? |
Breach response | Who investigates, who decides and who communicates? | Are there different notification deadlines or regulator forms? |
Retention | How long is data kept and why? | Do tax, employment, litigation or anti-money laundering rules require longer retention? |
A matrix like this gives legal, IT, compliance and operations a shared reference point. It also helps when global clients ask how privacy controls are managed across the business.
Make the choice work across governance and operations
A lead law only works if ownership is clear. The board or senior leadership should approve the baseline and risk appetite. Legal or compliance should interpret obligations. IT and security should support technical controls. Business units should apply the rules when they collect, use, share or delete personal data.
Training is also essential. Employees do not need to memorise every statute, but they should understand the organisation's baseline rules: when to escalate a new processing activity, how to recognise a rights request, what to do after a suspected breach and when vendor due diligence is required.
For global operations, customer assurance becomes part of the governance model. Overseas clients may ask whether your organisation has privacy policies, retention rules, breach procedures, security controls and vendor oversight. PLMC's guide on what global clients expect from your privacy controls explains these expectations in more detail.
The aim is consistency. A client in Toronto, London or Kingston should not receive three different explanations of your privacy programme unless a local law genuinely requires different treatment.
Contracts and vendors must reflect the baseline
Your chosen privacy baseline should appear in contracts, procurement documents and vendor onboarding. If the policy says processors must follow defined security, confidentiality, breach reporting and deletion rules, contracts should not be silent on those points.
This is especially important where Jamaican organisations work with overseas clients or global cloud providers. A mismatch between internal policies and contract wording creates avoidable risk. If a client asks for breach notice within a specific period, audit cooperation or restrictions on subcontracting, the organisation must know whether it can comply operationally before signing.
Data processing agreements should also distinguish between controller, processor, service provider and independent-controller roles. Those labels are not interchangeable, and different laws use different terminology. The contract should match the actual processing relationship.
For cross-border engagements, privacy clauses should address transfer mechanisms, assistance with rights requests, confidentiality, security measures, incident escalation, subcontractors and return or deletion of data. PLMC has a practical article on privacy clauses for contracts with overseas clients for organisations that need to tighten this part of the programme.
Red flags that the chosen lead law is not working
A lead law should make decisions clearer. If it creates confusion, the organisation may have selected the wrong baseline or failed to operationalise it.
Watch for these warning signs:
Policies refer to one law, but contracts promise another standard.
Staff cannot explain when a privacy impact assessment is required.
Vendor reviews are handled differently by each department.
Customer notices are rewritten for every market without a common template.
Data subject rights requests are treated as unusual events instead of routine processes.
The organisation has no documented reason for choosing its baseline.
Senior leadership assumes GDPR, Jamaica data privacy compliance or US privacy rules are automatically interchangeable.
These issues do not always mean the lead law itself is wrong. They may mean governance, documentation or training has not caught up with the decision.
Frequently Asked Questions
Is a lead privacy law legally binding? A lead privacy law is usually an internal governance choice, not a separate legal status. It helps the organisation design consistent controls, but the organisation must still comply with every law that applies to its activities.
Should a Jamaican company always choose Jamaica's Data Protection Act, 2020 as its lead law? Not always. Jamaican law should be a core requirement for organisations established or operating in Jamaica, but a business with heavy EU or UK exposure may choose GDPR or UK GDPR as the global baseline and treat Jamaica's Act as a mandatory local overlay.
Is GDPR always the best global privacy baseline? GDPR is a strong and widely recognised framework, but it is not automatically the best choice for every organisation. If the organisation has limited EU exposure, another baseline may be more practical, provided local and contractual obligations are still met.
How often should the lead law decision be reviewed? Review it when the organisation enters a new market, launches a new data-driven product, changes cloud providers, signs a major overseas client or faces a new regulatory requirement. An annual review is also sensible for mature governance programmes.
Who should own the decision internally? Senior leadership should approve the approach, with input from legal, compliance, IT, security, procurement, HR and business leaders. Privacy cannot sit with one department if personal data is used across the organisation.
Turn the lead law into a working privacy programme
Choosing a lead privacy law is a governance decision first, then a legal and operational exercise. The value comes from converting the chosen framework into policies, contracts, training, risk assessments, vendor controls and board-level reporting.
Privacy & Legal Management Consultants Ltd. supports organisations in Jamaica with data protection implementation, corporate governance, anti-money laundering compliance, cyber security services, GRC integration and privacy training. If your organisation is expanding globally, serving overseas clients or trying to align multiple privacy obligations, PLMC can help you build a practical compliance roadmap that fits your risk profile and operating model.