

A Simple Framework for Multi-Country Privacy Compliance
Multi-country privacy compliance becomes difficult when every new market creates another policy, spreadsheet and approval process. For Jamaican organisations serving overseas customers or using international suppliers, a more manageable approach is to maintain one core privacy programme, then add the requirements that apply to each jurisdiction.
The objective is not to make every country follow the same law. It is to give staff a consistent way to handle personal data while preserving local differences in consent, individual rights, retention, breach reporting and international transfers. This five-part framework turns those differences into practical controls with named owners and evidence.
The five-part framework for multi-country privacy compliance
Build your programme around five connected activities: map the processing, establish common controls, document local requirements, standardise workflows and retain evidence. Each activity should produce something staff can use, rather than another policy that remains unread.
1. Map processing activities and determine which laws apply
Start with business activities, not a list of countries. Customer support, recruitment, payroll, marketing and appointment booking may each involve different people, systems and legal obligations.
For each activity, record whose information you hold, why you need it, where it is collected, where it is stored and who can access it. Include remote access and supplier support, not just the physical location of a server.
Then distinguish three separate questions:
Legal scope: Which laws apply because of your establishment, activities, customers or sector?
Organisational role: Are you deciding why and how information is used, processing it for another organisation or doing both for different activities?
Data movement: Is information disclosed, transferred or made accessible across borders, and how does the relevant law classify that arrangement?
An overseas customer does not automatically bring every foreign privacy law into scope. Equally, operating from Jamaica does not prevent another jurisdiction’s law from applying.
For example, the GDPR’s territorial scope can extend to organisations outside the European Union when they offer goods or services to individuals in the Union or monitor their behaviour there. Citizenship alone is not the test.
Before entering a new market, use a structured process to assess overseas privacy laws before expansion. Record your scope decision and its reasoning, including situations where a law does not apply.
2. Establish a common set of privacy controls
Your common controls should cover practices that make sense across operations: collecting only necessary information, restricting access, keeping records accurate, protecting systems and deleting information when there is no longer a justified need to retain it.
For a Jamaica-based organisation, align these controls with obligations under the Data Protection Act, 2020. Check current regulatory guidance from the Office of the Information Commissioner and confirm any applicable registration, data protection officer and reporting requirements.
A practical baseline should include:
Collection controls: Document the purpose, required information and applicable lawful basis or other legal condition.
Transparency: Explain processing through appropriate privacy notices at the relevant collection points.
Access and security: Apply role-based permissions, suitable authentication and safeguards proportionate to risk.
Retention: Set schedules by record type, including legal holds and statutory retention duties.
Supplier management: Assess vendors before access is granted and define responsibilities in contracts.
Rights and incident handling: Provide clear routes for requests, complaints and suspected breaches.
Treat this baseline as a shared operational minimum, not proof of compliance everywhere. A GDPR-style policy does not automatically satisfy Jamaican, Australian or US requirements.
Avoid applying the “strictest rule” blindly. A deletion request, for instance, may need to be reconciled with a mandatory anti-money laundering retention obligation rather than handled through immediate erasure.
3. Add local requirements through a jurisdiction matrix
A jurisdiction matrix connects legal differences to the affected process. Keep it short enough for operational teams to use, with a more detailed legal assessment available behind it.
For each requirement, record the applicable activity, required control, accountable owner, supporting evidence and review date. These entries make multi-country privacy compliance easier to maintain when rules or suppliers change.
Jurisdiction or regime | What to verify | Operational consequence |
Jamaica | Applicable duties under the Data Protection Act, including overseas transfers and sensitive personal data | Document processing conditions, transfer safeguards and relevant regulatory obligations |
EU GDPR | Territorial scope, controller or processor role, individual rights and Chapter V transfer requirements | Add the required notices, contracts, request deadlines and transfer arrangements |
Australia | Privacy Act coverage, Australian Privacy Principles and relevant health-sector requirements | Check sensitive-information handling, overseas disclosure obligations and applicable breach rules |
United States | Relevant state privacy laws, sector-specific laws and their applicability thresholds | Apply requirements to the covered activities rather than assuming one national rule |
This is a starting checklist, not a complete statement of each jurisdiction’s law. Confirm current requirements and obtain qualified advice where scope or interpretation is uncertain.
Make the matrix specific. “Follow Australian privacy law” is not an actionable instruction. “The vendor approval process must assess applicable overseas disclosure obligations before patient information is shared” identifies a control staff can follow.
For covered Australian entities, the Australian Privacy Principles address matters including sensitive information and cross-border disclosure. Private health service providers can be covered even when they are small businesses, so turnover alone is not a reliable screening test.
Where requirements conflict, record a reasoned decision instead of silently choosing whichever rule appears stricter.
4. Turn the rules into shared workflows
Policies describe expectations. Workflows determine what happens when a supplier changes, someone requests their information or a security incident occurs.
Use one intake process for each recurring event, then route it according to the relevant jurisdiction and activity. This avoids separate country procedures that gradually drift apart.
Individual rights requests
Create a central request log with the date received, identity checks, relevant systems, responsible person and applicable deadline. Staff should identify the governing requirements before promising a response date.
Do not assume every jurisdiction provides identical access, correction, deletion or objection rights. Where information must be retained, explain the applicable restriction rather than treating the request as either automatically valid or automatically refused.
Supplier onboarding and international transfers
Before approving a supplier, check its processing locations, remote-access arrangements, subcontractors, security measures and deletion or return procedures. Distinguish the contract governing the service from any legally required international transfer mechanism.
Contract language alone does not establish that the supplier can meet its commitments. Pair contractual safeguards with proportionate due diligence and ongoing checks. Your legal and procurement teams can use privacy clauses for contracts with overseas clients to connect operational responsibilities with agreed terms.
Incident response
Use a single internal escalation route, followed by jurisdiction-specific assessments of whether authorities, affected people or clients must be notified.
Under the GDPR, a controller generally must notify the supervisory authority within 72 hours of becoming aware of a personal data breach, unless it is unlikely to result in a risk to individuals’ rights and freedoms. Other laws use different triggers and timelines. Record those differences in the response plan rather than applying a universal “72-hour rule”.
A worked example: Jamaican support for an Australian clinic
Consider a hypothetical Jamaican support company providing appointment administration for an Australian dental clinic. Practices such as Bright Smiles Dentistry on the Sunshine Coast offer online appointment booking, illustrating a service where patient contact information may be involved. The cross-border arrangement described here is hypothetical and does not describe that practice’s actual systems, suppliers or compliance.
Assume the support team needs names, contact details and appointment times, but has no business need to view clinical notes. The framework would translate that limitation into access permissions, staff instructions and a contract defining permitted processing.
The parties would then assess their respective roles and obligations. The clinic would examine applicable Australian requirements, including whether the arrangement engages overseas disclosure rules. The Jamaican company would assess its own obligations under Jamaican law and the contractual requirements attached to the service.
Finally, they would agree how the support team escalates an access request or incident, who makes notification decisions and what evidence each party retains. The same method works for other sectors, with different information types and local rules.
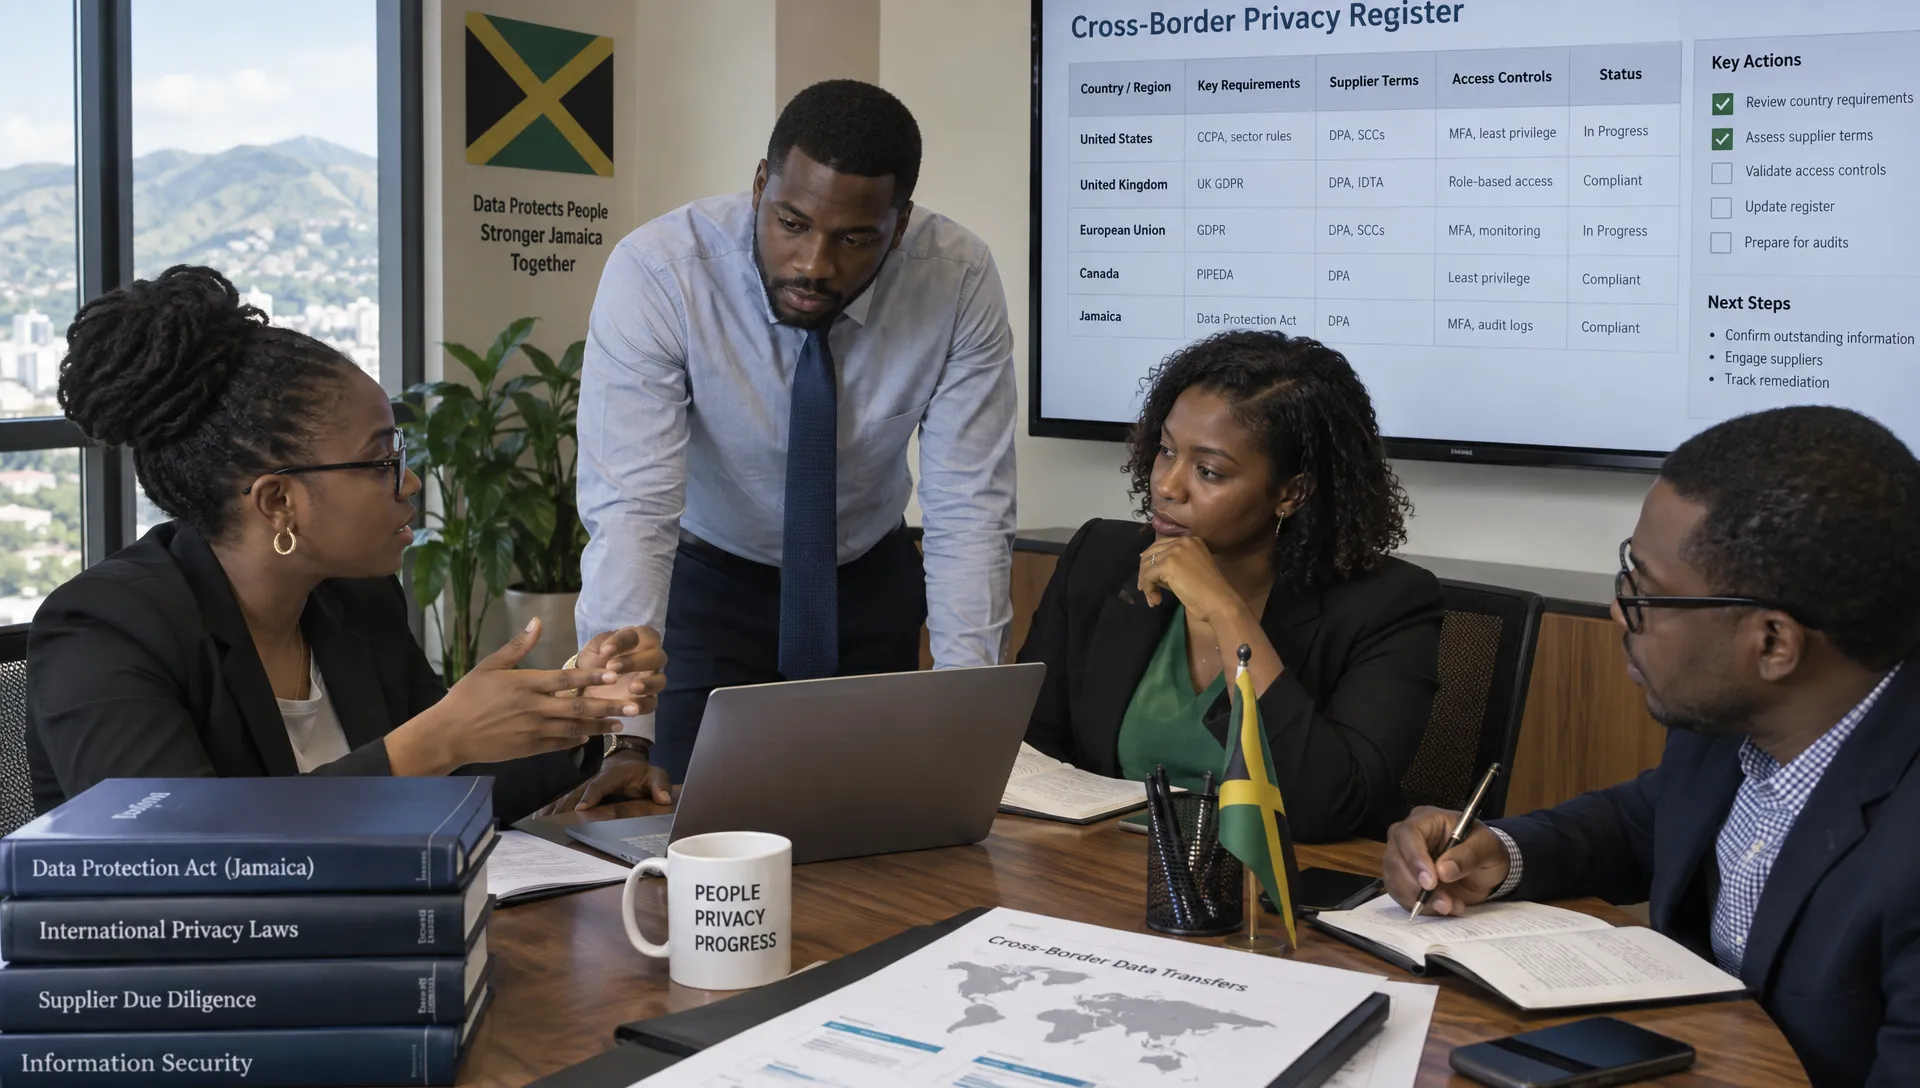
5. Keep evidence and review changes
A programme should demonstrate what happened, not merely what a policy says should happen. For each important control, identify the evidence that would show it operated as intended.
Useful records include approved privacy notices, completed supplier assessments, access reviews, training attendance, request logs, incident decisions and records of deletion. Keep evidence proportionate to risk and avoid retaining unnecessary personal information simply to prove compliance.
Assign operational ownership carefully. IT may implement access controls, HR may own employee records and procurement may manage supplier checks. A privacy lead coordinates the programme, but cannot perform every control personally.
Review the framework when processing changes, not just on an annual calendar. A new market, sensitive dataset, supplier location or automated decision-making tool should trigger reassessment. Carry out a privacy impact assessment when risk or an applicable legal requirement calls for one.
Track a few useful measures: overdue requests, suppliers awaiting assessment, unresolved high-risk findings and access reviews completed. These show whether multi-country privacy compliance is functioning in everyday work, rather than measuring how many policies have been written.
Put the framework into practice in 30 days
Treat the first month as a focused implementation sprint, not a promise of full compliance.
Week one: select a priority process. Choose an activity with cross-border exposure, such as customer support or cloud-based HR. Map its information, locations, suppliers and decision-makers.
Week two: establish the legal requirements. Confirm relevant jurisdictions and roles, then identify gaps between existing controls and applicable obligations. Prioritise sensitive information, weak access controls and unclear transfer arrangements.
Week three: test the workflows. Run a sample rights request, supplier approval and incident escalation. Check whether staff can locate records and reach the correct decision-maker without relying on informal knowledge.
Week four: capture evidence and assign remaining work. Record completed changes, unresolved issues, responsible owners and realistic deadlines. Expand to other processes once the approach works for the first one.
This phased approach gives management a clear view of progress without mistaking a completed checklist for a finished compliance programme.
Frequently asked questions
Does a Jamaican business automatically need to comply with the GDPR? No. Applicability depends on the GDPR’s scope rules and the business’s activities. Contractual requirements from an EU client may also apply, but those are not the same as being directly subject to every GDPR obligation.
Can one privacy policy cover several countries? A shared policy framework can support several markets, but local notices or supplements may be necessary. Ensure the documents accurately explain the relevant processing and rights instead of listing every country’s rules indiscriminately.
Does keeping data on a Jamaican server avoid international transfer issues? Not necessarily. Overseas access, supplier support and other disclosures may still require assessment. Map who can access the information and how the applicable law treats that access, rather than considering storage location alone.
Can an international security certification replace privacy compliance? No. A certification may support evidence of security controls, but it does not by itself establish lawful processing, adequate notices, compliant transfers or effective handling of individual rights.
Build a framework that fits your organisation
Start with one high-risk process and identify the country-specific requirements that your current controls do not address. That exercise gives you a practical basis for prioritising investment, training and legal review.
Privacy & Legal Management Consultants Ltd. supports organisations in Jamaica with data protection implementation, GRC integration, risk assessment and training. Arrange a free consultation with PLMC to discuss your cross-border activities and the next steps for a workable privacy programme.