How to Write a Risk Appetite Statement Your Board Can Use
A risk appetite statement should help your board make a difficult decision, not simply confirm that the organisation takes risk seriously. When management proposes a new service, a major supplier contract or a cost-saving measure, directors should be able to use the statement to decide whether to proceed, require stronger controls or stop.
For Jamaican organisations, that means connecting business objectives with financial resilience, service continuity and obligations such as the Data Protection Act, 2020. This guide explains how to draft a practical statement, set meaningful limits and establish what happens when those limits are approached or breached.
What a board-ready risk appetite statement must do
Risk appetite describes the types and amount of risk an organisation is willing to take in pursuing its objectives. A usable statement translates that willingness into decisions management can apply.
It should answer four questions: What are we trying to achieve? Which risks will we accept? Where are the boundaries? Who acts when exposure changes?
Before drafting, agree on terminology. Organisations sometimes use these terms differently, so record the definitions your board adopts.
Term | Practical meaning | Question for the board |
Risk appetite | The nature and level of risk the organisation is willing to take to achieve its objectives | What exposure are we prepared to accept? |
Risk tolerance | The permitted variation around an objective or appetite boundary | How far may performance or exposure move before stronger intervention is required? |
Risk capacity | The maximum exposure the organisation can bear without threatening its viability or essential obligations | What could we withstand, regardless of our willingness to take it? |
Risk limits | Specific operational boundaries used to implement appetite and tolerance | What measurable condition triggers action? |
The Financial Stability Board’s principles for an effective risk appetite framework provide a useful reference for these distinctions. They were developed for financial institutions, so other organisations should adapt the approach rather than treat it as a universal regulatory requirement.
Appetite must remain within capacity. A board’s willingness to accept a loss does not establish that the organisation has the cash, people or recovery capability to absorb it.
How to draft the statement in six steps
1. Start with strategic decisions, not risk labels
Ask which decisions the board expects to make over the next planning period. Expansion, digital services, outsourcing and investment usually involve different trade-offs.
A business seeking growth may accept uncertainty about customer demand but remain cautious about service disruption. Another may accept slower implementation to protect liquidity or meet compliance requirements.
Write those trade-offs in plain language before assigning labels such as “low” or “moderate”. For example:
We will accept limited uncertainty in demand when testing new services, provided investment is staged and the pilot does not weaken existing service commitments.
This gives management a direction. “We have a moderate appetite for strategic risk” does not explain what anyone should do differently.
2. Establish capacity and non-negotiable boundaries
Management should provide evidence of what the organisation can withstand. Depending on the business, that may include liquidity forecasts, available capital, recovery tests, staffing constraints and contractual commitments.
Separate commercial discretion from legal obligations. A risk appetite statement cannot authorise unlawful processing, excuse an anti-money laundering obligation or override another applicable legal requirement.
For data protection, distinguish between accepting uncertainty in a properly assessed activity and knowingly proceeding without a required lawful basis or safeguard. Directors cannot turn the latter into an acceptable business risk by approving it.
Use the Office of the Information Commissioner as an official starting point for Jamaican data protection guidance. Questions about how a requirement applies to a particular activity should go to the appropriate compliance or legal adviser.
3. Choose a small number of decision-relevant categories
Use categories that reflect the organisation’s actual choices. These may include strategic investment, financial resilience, service continuity, people, information security and regulatory compliance.
Avoid creating a separate appetite paragraph for every risk in the register. The statement should guide decisions across those risks, not reproduce the entire inventory.
For each category, explain both the opportunity and the boundary. For example:
We will consider outsourcing where it improves service capability, but we will not proceed until the proposed supplier’s access, security arrangements and continuity dependencies have been assessed and approved.
If privacy exposures are not yet consistently recorded, adding data protection to the risk register helps connect the board’s position to identifiable risks, controls and owners.
4. Set observable limits and early warnings
Words such as “minimal” and “cautious” need supporting criteria. Select indicators that show whether exposure is moving towards an unacceptable condition.
Useful measures may concern recovery capability, financial exposure, unresolved control weaknesses or activities awaiting approval. Include leading indicators, not just counts of incidents that have already happened.
For every measure, specify its scope, calculation, reporting period and source. “Supplier compliance: 95%” is not meaningful unless directors know which suppliers are included, what compliance means and whether the remaining 5% includes the most critical provider.
A practical structure distinguishes three states:
Within appetite: Management may proceed within approved controls and delegated authority.
Early warning: Exposure needs attention, a corrective plan or additional approval before it reaches a hard boundary.
Outside tolerance or a mandatory boundary: Management must take the specified containment action and escalate through the agreed route.
An early warning is not permission to continue indefinitely. Give it an owner, a deadline and a defined consequence if the position does not improve.
5. Assign decision rights and exception rules
A risk appetite statement is incomplete if everyone can identify a breach but nobody knows who may respond.
Name the accountable executive for each category, identify who can approve temporary deviations from internal limits and establish which matters require board or committee consideration. Oversight arrangements should reflect the organisation’s structure and applicable requirements.
Any exception process should record the reason, remaining exposure, compensating controls, authorised decision-maker and expiry date. Exceptions to internal policy must never be treated as permission to disregard law or mandatory requirements.
For data protection matters, the business owner remains responsible for the activity and its risks. The Data Protection Officer or relevant adviser provides advice and oversight appropriate to their role, rather than becoming the automatic owner of every privacy decision.
6. Test the draft against real proposals
Before approval, apply the draft to two or three decisions the organisation genuinely faces. Ask different executives to reach a decision independently using the same wording.
A proposed customer analytics service might offer commercial benefits but introduce a new use of personal data. Can the statement distinguish a properly assessed pilot from a proposal that lacks necessary permissions, safeguards or accountability?
Also test a stress scenario, such as a critical supplier failing during a period of cash pressure. Individually acceptable risks can combine into an exposure beyond the organisation’s capacity.
If the wording supports contradictory answers, revise it. The purpose is consistent judgement, not a document that can justify any outcome.
Worked example: a risk appetite statement for board approval
The following example is illustrative, not a recommended limit or a statement of legal requirements. It assumes a Jamaican service organisation introducing digital services while depending on third-party technology. Replace the assumptions and figures with evidence from your own operations.
Example board-approved wording
We will take measured commercial and technology risks to improve customer service and develop sustainable revenue. We prefer staged investments with defined review points and will not accept exposure beyond our demonstrated financial and operational capacity.
We have a low appetite for interruption to critical customer services. Management must maintain tested recovery arrangements and operate within the service limits in the approved schedule.
We will consider new uses of personal data only after applicable legal requirements and internal approval conditions have been satisfied. We have no appetite for knowingly unlawful processing, deliberate concealment of incidents or intentional circumvention of mandatory controls.
Management must monitor agreed indicators, act on early warnings and escalate breaches through the approved authority structure. Acceptance of residual risk must be documented and remain within the decision-maker’s delegated authority.
This wording allows controlled innovation without suggesting that growth can override compliance. It also avoids the unrealistic promise that no incident will ever occur.
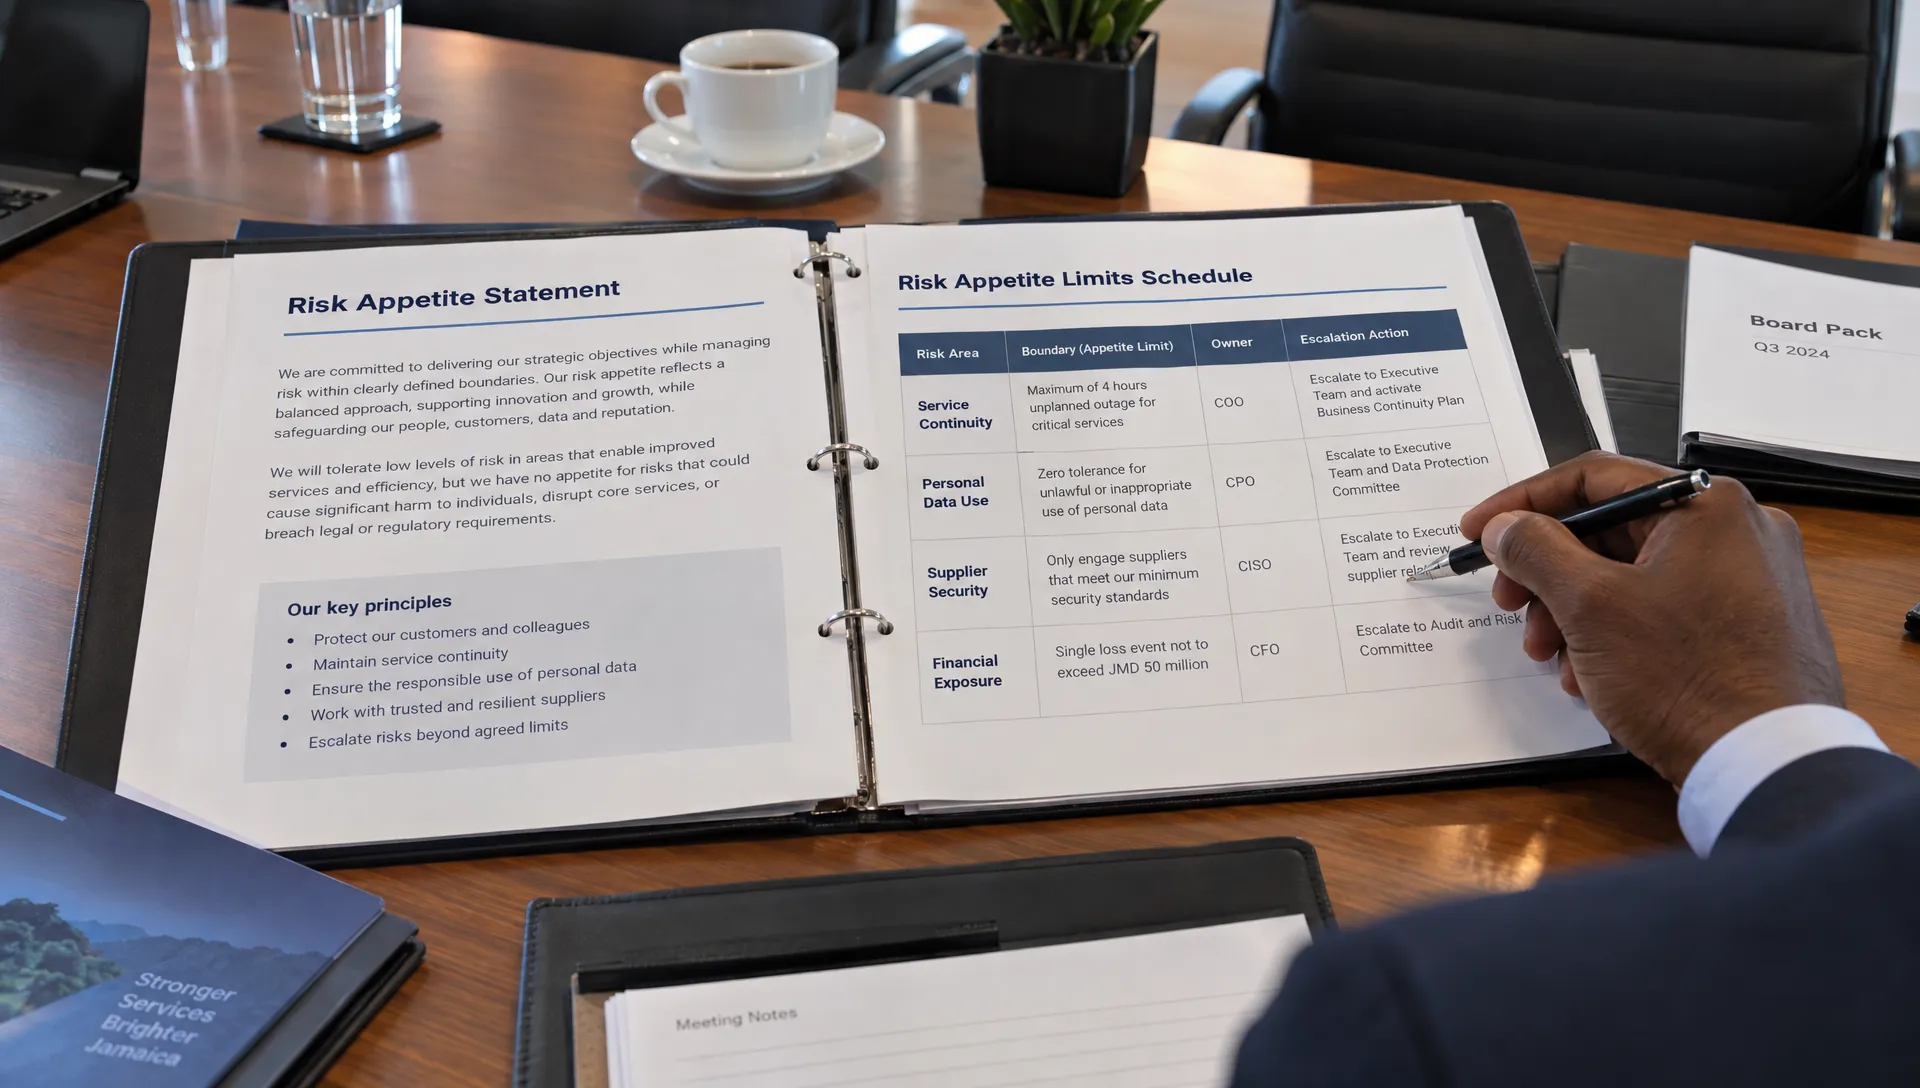
Illustrative limits schedule
Keep detailed limits in a controlled schedule linked to the statement. This makes the board’s position readable while preserving the operational detail needed to apply it.
Risk area and measure | Preferred position | Early warning | Boundary requiring escalation |
Critical-service interruption, measured per event | No more than 30 minutes | More than 30 minutes, up to 60 minutes | More than 60 minutes, with incident response continuing throughout |
Proposed high-risk uses of personal data | Required legal conditions, safeguards and internal approvals satisfied before launch | Approval or assessment remains incomplete as the planned launch approaches, so launch stays on hold | An activity is live without a required legal condition or safeguard, requiring prompt containment and assessment |
Critical supplier security findings, using an approved severity definition | No known unresolved critical findings affecting the live service | A critical finding is identified before launch or renewal and remains unresolved | A critical finding affects an existing live service, requiring immediate assessment, containment and escalation |
The interruption figures are examples only. A safety-critical service may need much tighter limits, while a less time-sensitive service may justify different ones. The schedule must also define the service, measurement method, owner and notification route.
A threshold never delays necessary action. A serious incident may require escalation before a numerical limit is reached. Legal notification duties must be assessed independently of internal reporting thresholds.
Show how the statement changes a decision
Suppose management proposes launching a customer portal next month. The commercial case is sound, but supplier assurance is incomplete and the proposed use of customer information has not received the necessary assessment and approval.
Under the example statement, the board could approve further development expenditure while withholding authority for a live launch. Management would receive clear conditions: complete the required assessment, resolve supplier concerns and present evidence to the designated approver.
That is more useful than either an unconditional approval or a general instruction to “manage the risks”. It separates permission to prepare from permission to expose customers and the organisation to a live activity.
Make the statement part of board decisions and reporting
Approval is the beginning of implementation. Add an appetite assessment to papers seeking material decisions: identify the relevant category, describe current and proposed residual exposure, state whether it falls within appetite and explain any exception requested.
The assessment should reflect the controls that will actually operate. A planned safeguard should not be presented as an effective control before it has been implemented and, where appropriate, tested.
Board reporting should then show movement against the approved limits. Directors need to see the trend, the reason for any deterioration, the responsible owner and the decision required. A green dashboard without supporting definitions or reliable evidence offers little assurance.
For privacy-related reporting, use board-level data protection KPIs and KRIs that connect control performance and emerging exposure to the boundaries directors have approved.
Review the risk appetite statement on an agreed cycle and when significant changes occur. Acquisitions, new processing activities, major incidents, funding pressures or new regulatory requirements may change what the organisation can reasonably accept. The review frequency is a governance choice unless a specific applicable requirement sets it.
A final approval checklist for directors
Before approving the document, directors should be able to confirm the following:
Each appetite position connects to an organisational objective and a recognisable decision.
Proposed exposure remains within demonstrated capacity and applicable legal boundaries.
Limits have clear definitions, reliable evidence sources and accountable owners.
Warning conditions, breaches and temporary exceptions have distinct response rules.
Delegated authority, escalation routes and review arrangements are documented.
Management has tested the wording against realistic proposals and combined-risk scenarios.
If directors cannot apply the document without asking its author what it means, it needs another draft. Keep the main statement short enough to use in a meeting, with supporting definitions and limits available alongside it.
Frequently asked questions
How long should a risk appetite statement be? The core statement can often fit on one or two pages, supported by a limits schedule. Length matters less than whether directors and management can apply it consistently without searching through unrelated policy material.
Should the board approve every limit? The board should approve the overall appetite and material boundaries. More detailed operating limits may be delegated within that framework, subject to applicable requirements and the organisation’s authority structure. Delegated limits must not weaken board-approved boundaries.
Can an organisation have zero appetite for compliance risk? It can state that it will not knowingly disregard legal obligations or deliberately bypass mandatory controls. That is different from claiming that errors, incidents or regulatory uncertainty will never occur. Monitoring and response arrangements remain necessary.
What happens when a limit is breached? The owner should follow the agreed response, assess immediate harm, contain exposure where appropriate and notify the designated authority. Record the cause, corrective action and conditions for returning within limits. Assess legal reporting duties separately.
Turn the draft into a usable governance tool
Bring together the board sponsor, finance, operations and relevant risk, compliance and legal advisers before seeking approval. Their task is to agree credible trade-offs and workable boundaries, not simply polished wording.
For support connecting corporate governance, data protection and risk management, Privacy & Legal Management Consultants Ltd. offers GRC services and free consultations. Use an initial discussion to identify where your current approach needs clearer limits, ownership or escalation rules.